Connect with us

Technology

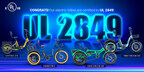
Addmotor Gets More Electric Tricycles Certified to UL 2849 System Safety Standard

Published

on

Enjoy Enhanced Safety on Every Ride with Newly Certified Electric Trikes

EL MONTE, Calif., July 2, 2024 /PRNewswire/ — Addmotor, America’s leading e-bike brand, proudly announces a significant milestone in product safety and quality assurance. Four of its premier electric trike models—the GRANDTAN E-Trike, CITYTRI Standard, ARISETAN M-360, and TRIKETAN M-330—have now been officially certified to the rigorous UL 2849 System Safety Standard.

This certification aligns with the company’s commitment to providing innovative, safe, and reliable transportation solutions for all users.

What the UL 2849 Certification Means

The UL 2849 certification is an industry benchmark for electrical system and battery safety for electric bikes and trikes. Achieving this certification involves a comprehensive evaluation process where each model undergoes extensive testing to ensure it meets the highest possible safety standards. These tests include assessing the durability and robustness of the electrical insulation, the effectiveness of the safety features under extreme conditions, and the reliability of the battery management systems to prevent overheating and ensure stable performance.

By adhering to these standards, Addmotor ensures its trikes offer enhanced safety features that protect against electrical hazards and battery malfunctions and contribute to safer riding experiences overall. The company prioritizes user safety and understands that its customers trust it to provide not only fun and functional mobility solutions but also ones that ensure their well-being and peace of mind on every ride.

Trike Models Boasting UL 2849 Certification

GRANDTAN E-Trike: Acclaimed for its ergonomic design and versatility, the GRANDTAN E-Trike is ideal for outdoor enthusiasts and senior citizens alike. In addition to its robust construction and powerful motor system, this trike has a user-friendly interface and efficient braking systems to accommodate riders of all skill levels. Its UL 2849 certification underscores its durability and safety, ensuring it is a dependable choice for both leisure and daily activities.

CITYTRI Standard:  As a model designed for urban environments, the CITYTRI Standard folding electric trike offers an exceptional combination of comfort and convenience. It’s compact and agile and is equipped with high-visibility lighting and advanced braking systems to enhance rider safety at night, in low-light conditions, and high-traffic areas. Its compliance with the UL 2849 standards ensures that it meets the rigorous demands of city commuting.

ARISETAN M-360:  The ARISETAN M-360 is known for its ergonomic design and superior back support, catering to users with mobility issues or chronic back pain. Its semi-recumbent frame and handlebar allow for further customization of rider ergonomics. UL certification enhances this trike’s appeal to a demographic that values safety as much as comfort.

TRIKETAN M-330:  The TRIKETAN M-330 is a fat tire electric trike that provides stability and traction on all types of terrain. It comes with a powerful 750W rear motor and a reinforced frame for increased durability and sturdiness on rough and uneven surfaces. Its certification highlights Addmotor’s commitment to delivering products that perform safely under diverse conditions.

Enhancing Consumer Confidence Through and Through

With the UL 2849 certification, Addmotor aligns itself with the best practices in electric bike safety and reinforces the trust placed in them by thousands of users across the United States. Customers purchasing these certified models can be assured of their quality, safety, and compliance with the latest industry standards. They can enjoy peace of mind, knowing that they are riding on some of the safest electric trikes available on the market today.

As Addmotor continues to lead and expand its offerings, it engages in ongoing research and development to further enhance the safety features of its bikes and trikes, ensuring that it stays at the forefront of technological advancements in the e-bike industry. This proactive approach to safety helps build a culture of trust and reliability around Addmotor’s products, encouraging more people to embrace the benefits of electric bikes and trikes without compromising safety.

For more information about Addmotor and its UL 2849-certified electric trikes, please visit www.addmotor.com.

About Addmotor:

Addmotor  is a leading name in the electric vehicle industry, specifically noted for its comprehensive range of electric bikes and trikes. Since its inception in 2011, the company has evolved from manufacturing motorcycle parts to specializing in electric bicycles, aligning with the global shift towards more eco-friendly and accessible transportation solutions.

Addmotor’s collection includes rugged mountain bikes for off-road adventures, sleek road bikes for urban commuting, and electric trikes for senior riders. The brand is dedicated to maintaining high-quality standards across all its products, which is evident in its meticulous construction, choice of durable materials, and rigorous testing processes.

View original content to download multimedia:https://www.prnewswire.com/news-releases/addmotor-gets-more-electric-tricycles-certified-to-ul-2849-system-safety-standard-302187783.html

SOURCE Addmotor Electric Bike

Continue Reading

Technology

ATMOCE Extends Australian M-ELV 7 kWh Battery Warranty to 15 Years

Published

on

By

New 15-year warranty covers all MS-7K-U units already shipped to Australia

SYDNEY, Oct. 20, 2026 /PRNewswire/ — ATMOCE Australia and New Zealand has extended the standard Australian warranty for its M-ELV 7 kWh Battery (MS-7K-U) from 12 to 15 years.

The new warranty provides 15 years or 29.2 MWh of energy throughput, with a minimum of 60% SOH retained, whichever comes first. It applies Australia-wide without regional restrictions and extends to all MS-7K-U units already shipped to Australia.

The warranty extension applies across Australia, including to customers who have already purchased the applicable products. The 15-year warranty period is calculated from the original warranty start date.

The change places ATMOCE in the longest standard-warranty tier in the Australian residential battery market, backed by 29.2 MWh of warranted energy throughput.

The extension comes as ATMOCE approaches its first anniversary in Australia and prepares to showcase the next stage of its Extra-Low Voltage energy platform at All Energy Australia 2026 in Melbourne later this month.

“Extending the MS-7K-U warranty to 15 years is another step in our commitment to the Australian market,” said Zebb Wilson, Sales Director at ATMOCE ANZ.

“It reflects the confidence we have in the technology and gives customers and industry partners greater certainty around the long-term value of the system. As we continue to invest in product development and long-term system performance, we want the support behind our products to reflect that same commitment.”

Designed for Long-Term Residential Energy Storage

The MS-7K-U is built around ATMOCE’s Extra-Low Voltage architecture, operating at 25.6 V DC, and uses an AC-coupled design suited to both new installations and retrofit applications.

The architecture supports single- and three-phase systems and integration with third-party photovoltaic (PV) inverters, giving installers greater flexibility when designing or upgrading residential energy systems.

For installers and channel partners, the warranty extension provides additional certainty when discussing system longevity, product support and whole-of-life value with customers.

“Warranty is increasingly part of the conversations installers are having with customers,” said Grant Behrendorff, Managing Director and Co-Founder at AC Solar Warehouse.

“Moving to 15 years gives installers greater confidence in the long-term proposition they are putting in front of homeowners.”

Safety Backed by Independent Fire Testing

The extended warranty sits alongside ATMOCE’s focus on safety at the system architecture level.

The MS-7K-U has undergone independent fire testing. During testing, one battery cell was forced to 233 °C and ignited, with the test recording no explosion, no pack-wide thermal runaway and no gas released outside the battery enclosure.

The battery uses lithium iron phosphate (LFP) cells supported by three layers of protection: intrinsic, passive and active.

Intrinsic protection begins with the system’s 25.6 V nominal Extra-Low Voltage DC architecture, with a fire-suppression device designed to activate at approximately 170 °C while active protection monitors voltage, current, temperature and insulation.

Together, these measures are designed to provide multiple layers of protection throughout system operation.

ATMOCE Returns to All Energy Australia

ATMOCE will return to All Energy Australia 2026 at Booth EE101, Melbourne Convention and Exhibition Centre, 28–29 October, showcasing its Extra-Low Voltage technology platform and joining industry partners for sessions on safety, system simplicity, Virtual Power Plant (VPP) participation and interoperability. Sessions will include Glen Morris and OpenSolar addressing Smart Energy Council Installer Roadshow FAQs and system design, a discussion on safer and simpler solar storage for New Zealand, and a session with AC Solar Warehouse exploring what installers need from battery storage.

For more information about ATMOCE and its energy storage technology, visit www.atmoce.com/au

About ATMOCE

Founded in 2024 and headquartered in Germany, ATMOCE is a global energy technology company committed to “Creating a Better World with Renewable Energy”.

ATMOCE develops integrated solar generation, energy storage and intelligent energy management technologies designed to help homeowners and businesses achieve greater energy independence. Through continuous innovation and a growing global partner ecosystem, ATMOCE is working to make renewable energy safer, smarter, simpler and more connected.

View original content to download multimedia:https://www.prnewswire.com/apac/news-releases/atmoce-extends-australian-m-elv-7-kwh-battery-warranty-to-15-years-302913827.html

SOURCE ATMOCE

Continue Reading

Technology

EMA Webinar Examines the Growing Friction Between AI Adoption and Enterprise Security

Published

on

By

New EMA research finds that 82% of IT and security leaders have experienced AI deployment delays due to security or compliance reviews, while organizations are limiting agent capabilities to accelerate adoption

LAFAYETTE, Colo., Oct. 20, 2026 /PRNewswire/ — Enterprise Management Associates (EMA™), a leading IT research and consulting firm, today announced The State of AI Friction: Delayed, Diminished, and Ungoverned AI, a live webinar examining the security and governance challenges slowing enterprise AI adoption and limiting its potential. The webinar will feature Christopher M. Steffen, VP of Research covering information security, risk, and compliance management at EMA, and James Rice, VP of Product Marketing and Strategy at Protegrity.

In a study conducted for Protegrity, EMA surveyed 152 IT and security leaders and found that 82% have experienced security or compliance reviews delaying AI deployment. Two-thirds of these delays last a month or longer, creating a growing challenge for organizations trying to move AI initiatives from experimentation to production while keeping pace with rapid advances in AI capabilities.

The pressure to deploy AI faster creates a second challenge: organizations may be limiting AI’s capabilities or operating agents without adequate safeguards. The study found that 81% have deployed AI agents with tools disabled or autonomy restricted to accelerate production deployment. At the same time, 69% already run agents that write to databases and trigger external APIs, introducing risks that traditional data security controls may not adequately address.

Encryption, data masking, and role-based access remain important safeguards, but organizations must also account for how autonomous agents access data, execute actions, and interact with enterprise systems. As organizations expand their AI initiatives, the gap between agent capabilities and existing security and governance controls becomes increasingly difficult to ignore. With 88% of respondents planning to increase agentic AI budgets by at least 10% next year, addressing this gap will be critical to realizing the value of those investments.

“Security teams aren’t trying to slow AI down, but the review processes most organizations rely on weren’t built for systems that act on their own. When the choice comes down to waiting months or switching off the capabilities that make agents valuable, nobody wins,” said Steffen. “Organizations need security and governance controls that move at the speed of AI, not the speed of a review cycle.”

During the webinar, Steffen and Rice will examine the research findings and discuss:

The business impact of AI delays: How extended security reviews affect deployment timelines and the ability to keep pace with a rapidly evolving AI landscape.The hidden cost of constrained AI: Why limiting agent tools and autonomy can undermine the value organizations expect from their AI investments.The security gap surrounding AI agents: Where traditional data protection approaches fall short as agents access sensitive information and take actions across enterprise systems.A path to secure AI in production: EMA’s recommendations for aligning security and governance controls with the capabilities and risks of agentic AI.

The webinar will take place Tuesday, October 27, 2026 at 1:00 p.m. Eastern. Registration is available at https://info.enterprisemanagement.com/the-state-of-ai-friction-webinar-pr

About EMA 
Founded in 1996, EMA is a leading IT research and consulting firm dedicated to delivering actionable insights across the evolving technology landscape. Through independent research, market analysis, and vendor evaluations, we empower organizations to make well-informed technology decisions. Our team of analysts combines practical experience with a deep understanding of industry best practices and emerging vendor solutions to help clients achieve their strategic objectives. Learn more about EMA research, analysis, and consulting services at www.enterprisemanagement.com and follow them on X and LinkedIn.

Media Contact:
Raleigh Gould
Enterprise Management Associates
rgould@enterprisemanagement.com

View original content to download multimedia:https://www.prnewswire.com/news-releases/ema-webinar-examines-the-growing-friction-between-ai-adoption-and-enterprise-security-302912219.html

SOURCE Enterprise Management Associates

Continue Reading

Technology

Teradata Introduces New Privacy, Security, and Resiliency Capabilities as AI Forces Change in Enterprise Data Protection

Published

on

By

New capabilities protect the sensitive data and intelligence behind enterprise AI while keeping mission-critical operations available and recoverable

SAN DIEGO, Oct. 20, 2026 /PRNewswire/ — Teradata (NYSE: TDC) today announced new privacy, security, and resiliency capabilities designed to address one of the defining challenges of enterprise AI: how sensitive data is protected, who and what can access it, and whether it remains available and recoverable when something goes wrong. Teradata addresses all three through an integrated approach that reduces raw identity exposure, enforces protection closer to the data, and keeps the intelligence powering AI available and recoverable. In practice, that means protecting the intelligence behind AI without diminishing what makes it valuable.

Key Capabilities

Poly-Anonymization®: reduces raw identity exposure while preserving the relationships and utility AI and analytics requireFormat-preserving encryption: protects sensitive values without changing their format or breaking downstream systemsPost-quantum security and readiness: strengthens protection against emerging quantum-era threats through Anonomatic PII Vault® and TLS 1.3 hybrid-key exchange for data in transitImmutable backup protection: prevents recovery points from being modified or deleted, strengthening cyber-recovery readinessDatabase-level high availability: an additional availability layer for mission-critical workloads, distinct from disaster recovery

Why It Matters Now
As AI becomes mission-critical, it expands both the value and the vulnerability of enterprise data. Sensitive information now moves among users, applications, models, and agents, making it harder to secure at the boundary alone. AI is designed to combine disparate information to find patterns and make decisions, which means data that isn’t individually identifiable can become so when AI brings it together.

Executive Quote
“Privacy, security, and resiliency have historically been treated as separate problems with separate solutions. That approach doesn’t hold up when AI is moving sensitive data across users, applications, models, and agents simultaneously. This announcement reflects how we think those capabilities need to work together, and it’s the foundation for how we intend to extend that protection as AI environments grow more complex and the actors operating within them multiply.”
          -Sumeet Arora, Chief Product Officer, Teradata

Privacy Protection
Access control determines who can see sensitive data. Identity reduction changes how much identifying information needs to be present in the analytical environment in the first place. Teradata combines both, through an OEM partnership with Anonomatic, whose privacy capabilities are natively available to Teradata customers.

Poly-Anonymization replaces PII fields with a stable identifier while holding underlying identity separately within Anonomatic PII Vault, a post-quantum-secure environment built with multiple layers of overlapping security controls designed to protect sensitive identity information. Authorized users can restore identity when a legitimate use case requires it, but everyone else works with data that retains its analytical structure, its relationships, and its utility. The result is an analytical environment where sensitive data can be used for AI, analytics, testing, and approved collaboration without broadly exposing who the data is about.

Unlike approaches that rely solely on mathematically reversible encryption, PII Vault combines identity separation, Poly-Anonymization, access controls, and additional layered protections to reduce identity exposure while retaining the utility required for AI and analytics. Format-preserving encryption extends that protection to situations where a value’s structure matters to downstream systems, protecting sensitive data without breaking the applications and workflows built around it.

Testing at large scale demonstrated that Teradata’s Anonomatic-powered privacy-preserving controls can support enterprise analytical workloads without the performance tradeoffs organizations typically associate with data privacy. Multi-table join queries on protected data used fewer Teradata resources than equivalent queries on unprotected data, though results will vary by workload and configuration.

Partner Quote
“Enterprise AI creates a fundamentally different privacy challenge. Organizations need to use sensitive, individual-level data to build effective AI, but the traditional tools for protecting that data weren’t designed to preserve what AI needs to work. Our partnership with Teradata makes it possible to reduce identity exposure at enterprise scale without forcing organizations to choose between protection and utility.”
          -Matt Fleck, Founder and CEO at Anonomatic, a data security software company focused on making PII data privacy secure, simple and cost effective

Native Data Security
Protection that follows the data requires controls enforced at the data layer, not just at the systems surrounding it. Teradata applies classification, policy enforcement, and access controls closer to the data itself. Together, these capabilities provide a governance-led foundation for protecting data and intelligence across users, applications, and workloads.

For data in transit, Teradata introduces post-quantum protection via TLS 1.3 hybrid-key exchange, which combines classical and post-quantum cryptographic algorithms in a single handshake. As quantum computing advances make current encryption standards increasingly vulnerable, organizations that establish cryptographic readiness now will be better positioned for what’s ahead.

New native capabilities including dynamic data masking, data classification and tagging, column-level encryption, and global identity extend that protection across the data layer. Through a partnership with Immuta, a data authorization platform between identity and enterprise data, dynamic ABAC brings identity-aware, attribute-driven access control that enforces policy consistently across users and AI workloads without duplicating data or rewriting governance rules.

Teradata’s security architecture is designed to extend as AI environments evolve, with ongoing investment in controls that govern how AI agents access and act on enterprise data within policy boundaries.

Enterprise Data Protection
For enterprises running AI at scale, a cyberattack is a threat to the data, context, and operational knowledge that AI depends on to function. Teradata Enterprise Data Protection addresses that reality through a workload-aligned approach that lets organizations match protection levels to business criticality rather than applying the same resiliency architecture to every workload. The objective is not simply to restore data, but to restore the trusted context AI needs to resume mission-critical operations.

Database-level high availability via real-time replication introduces an additional availability layer designed for continuous synchronization and low recovery objectives.

Immutable backup protection strengthens cyber-recovery readiness by ensuring recovery points cannot be modified, encrypted, or deleted, even by privileged administrators. As ransomware increasingly targets backup data specifically, protected recovery points have become as critical as the protection strategies built around them. Teradata’s resiliency architecture is designed to extend as cyber threats and recovery requirements evolve.

Additional capabilities including backup and recovery, scheduled data synchronization, and disaster recovery round out a more consistent Enterprise Data Protection experience.

Availability

Privacy capabilities, powered by Anonomatic and delivered by Teradata, are available now for Teradata Cloud on AWS, Azure, and Google Cloud.Native data security capabilities including dynamic data masking, data classification and tagging, and column-level encryption are available on Teradata Cloud across AWS, Azure, and Google Cloud. Dynamic data masking, data classification and tagging are available for Teradata Factory and on-premises deployment options.Teradata Enterprise Data Protection including immutable backup protection is available now on Teradata Cloud across AWS, Azure, and Google Cloud with availability on Teradata Customer Cloud planned in the coming months. 

About Teradata
Teradata empowers enterprises to turn intelligence into autonomous action, grounding AI agents in deep business context and trusted data. As AI agents multiply, Teradata is the context foundation, governance layer, and performance backbone that companies need now. The Teradata Autonomous Knowledge Platform puts AI into production across cloud, on-premises, and hybrid environments.

Forward-Looking Statements
This press release contains “forward-looking statements” about the expectations, beliefs, plans, and intentions relating to Teradata’s privacy, security, and resiliency capabilities. Such statements include statements regarding future product availability, capabilities, and offerings, and expected benefits to Teradata customers. Forward-looking statements are subject to known and unknown risks and uncertainties and are based on potentially inaccurate assumptions that could cause actual results to differ materially from those expected or implied by the forward-looking statements. If any such risks or uncertainties materialize or if any of the assumptions prove incorrect, Teradata’s results could differ materially from the results expressed or implied by the forward-looking statements made. Teradata undertakes no obligation, and does not intend to update the forward-looking statements. Factors that may cause actual results to differ materially from those in any forward-looking statements include: (i) delays and unexpected difficulties and expenses in executing the planned product capabilities and offerings, (ii) changes in the regulatory landscape related to AI and (iii) uncertainty as to whether customer adoption will justify the investments in the product capabilities and offerings. Further information on factors that could affect Teradata’s financial and other results is included in the filings Teradata makes with the Securities and Exchange Commission from time to time.

The Teradata logo is a trademark, and Teradata is a registered trademark of Teradata Corporation and/or its affiliates in the U.S. and worldwide.

Poly-Anonymization and PII Vault are registered trademarks of Anonomatic, Inc.

MEDIA CONTACT
Jennifer Donahue
Jennifer.Donahue@Teradata.com

View original content:https://www.prnewswire.com/news-releases/teradata-introduces-new-privacy-security-and-resiliency-capabilities-as-ai-forces-change-in-enterprise-data-protection-302913579.html

SOURCE Teradata

Continue Reading

Trending