Connect with us

Technology

Zest AI Debuts AI-Powered Fraud Detection for Lenders

Published

on

Zest Protect helps lenders decision loans more confidently with accurate, holistic application fraud detection 

LOS ANGELES, Aug. 7, 2024 /PRNewswire/ — Zest AI, the leader in AI lending technology, today announced its new fraud detection solution, Zest Protect. Zest Protect quickly and accurately identifies fraudulent activity during the loan decisioning process, helping credit unions, banks and other lenders navigate the rising application fraud environment while safeguarding the borrower experience.

The Federal Trade Commission estimates that consumer fraud losses in 2023 exceeded $10 billion while credit unions and community banks reported a 69% surge in fraud cases across consumer accounts.

“Lenders need to outsmart fraud, including an increasing volume of AI-driven fraud in the industry, with AI,” said Adam Kleinman, Head of Strategy and Client Success at Zest AI. “Our team designed Zest Protect to create an efficient tool that can more accurately detect all types of fraud now and in the future, including AI-created fraud, with the ultimate goal of boosting lending confidence for our bank and credit union customers.”

Zest Protect leverages Zest AI’s proven, industry-leading machine learning technology to instantly detect first party and third party fraud, as well as flag income inconsistencies within the automated loan decisioning process. This integrated solution empowers lenders to take control of their fraud risk, allowing them to adjust specific detection thresholds based on their risk tolerances and automation objectives. With access to fraud prevention data and analytics, Zest AI can flag applications swiftly, and protect against emerging threats. 

“Capturing application fraud, especially more sophisticated AI-powered fraud, without compromising the member experience is a top priority for us,” said Gather Federal Credit Union’s EVP, Justin Ganadan. “The insights, accuracy and end to end automation we have experienced with Zest AI technology has transformed our lending business. We’re excited to bring that same level of innovation and intellectual rigor to fraud prevention with Zest Protect.”

“The banking industry is bracing for an onslaught of fraud as AI tools become more ubiquitous, making it easier to generate deepfakes, clone voices and otherwise defraud people and businesses,” said Zest AI CEO Mike de Vere. “Now with a combination of AI-automated underwriting technology and fraud detection, we can enable lenders to safely and efficiently fund more loans.”

Zest Protect has been piloted with select Zest AI credit union customers. For more information about the availability of Zest Protect, please contact us via our contact form on Zest AI.

About Zest AI‍
Zest AI is a tech company on a mission to broaden access to equitable lending. Since 2009, we’ve worked with financial institutions to use AI lending technology to better serve their borrowers. Today, we work with all types of lenders as a catalyst for economic equity by helping them leverage AI’s potential for good. Most recently we were named to the Forbes Fintech 50. Learn more at Zest AI and connect with us on LinkedIn.

View original content to download multimedia:https://www.prnewswire.com/news-releases/zest-ai-debuts-ai-powered-fraud-detection-for-lenders-302216087.html

SOURCE Zest AI

Continue Reading

Technology

Nozomi Networks Lands Co-Development Project with Lockheed Martin to Strengthen Cybersecurity for Government and Defense Environments

Published

on

By

Lockheed Martin is providing offset funding and technical expertise to support Nozomi Networks in developing advanced cybersecurity and automated security configuration assessment capabilities for diverse, distributed environments, starting with DISA STIG compliance.

SAN FRANCISCO and MENDRISIO, Switzerland, Nov. 17, 2026 /PRNewswire/ — Nozomi Networks Inc., the leader in AI-powered operational technology (OT), Internet of Things (IoT), and cyber physical security (CPS), today announced a strategic collaboration with Lockheed Martin (NYSE: LMT) to accelerate and simplify how global government and defense organizations secure their environments and demonstrate configuration compliance across defense networks.

As an offset project tied to the F-35 sale to Switzerland, Nozomi Networks developers, supported by Lockheed Martin cyber experts, are building significant new capabilities within the Nozomi Networks platform. These enhancements will enable the safe automation of security configuration assessments (SCAs) across diverse, distributed environments while simplifying configuration compliance and reporting tasks. The collaboration will enable government and defense industrial base organizations globally to:

Automate configuration compliance assessments and reporting against established benchmarks such as Defense Information Systems Agency (DISA) Security Technical Implementation Guides (STIGs)Safely extend automated configuration compliance checks to OT and cyber-physical systems that cannot tolerate traditional, IT-centric assessment techniquesMerge configuration compliance reporting tasks with advanced asset identification, threat detection, and risk analysis capabilitiesProduce repeatable, auditable evidence of configuration compliance to support DoD Risk Management Framework (RMF) and authorization activities

The first of these capabilities is automated SCA, initially mapped to DISA STIGs. Existing STIG assessment workflows were designed for laptops, servers, and enterprise infrastructure and are less effective for engineering workstations, facility systems, and other operational assets that may not tolerate traditional assessment techniques. As a result, many defense organizations still rely on spreadsheets and manual validation to demonstrate compliance, an approach that cannot scale as frameworks such as the DoD Control Systems Security Requirements Guide (SRG) extend cybersecurity requirements to industrial control and cyber-physical systems.

Using Nozomi Arc sensors, organizations can safely collect host-level configuration data to evaluate endpoints against DISA STIG benchmarks, also supported by passive monitoring of network communications. Assessment results are consolidated and centrally managed, either on premises in the Nozomi Networks Central Management Console (CMC) or in the cloud through Vantage or Vantage for Government. Security teams can track compliance posture and changes over time, review pass/fail findings and supporting evidence, investigate rule-level findings and remediation guidance, and view configuration posture alongside asset inventory, vulnerability, and risk data.

DISA STIGs are only the beginning. Nozomi Networks plans to add safe active polling to collect configuration data from assets where endpoint sensors can’t be deployed and to extend the platform to additional security frameworks and benchmarks across OT, IoT, and IT environments.

“This work with Lockheed Martin is a testament to our joint commitment to bringing the power of AI to improve how our public-sector customers secure their systems,” said Nozomi Networks CEO Andrea Carcano. “With automated DISA STIG assessments, defense organizations can now validate configuration compliance across diverse environments safely and at scale, without the spreadsheets and manual processes that have held them back. We are proud to take this important, industry-leading step with Lockheed Martin to deploy the most advanced AI tools to support government agencies while adhering to the highest standards of cybersecurity governance.”

About Nozomi Networks
Nozomi Networks protects the world’s critical infrastructure from cyber threats. Our platform uniquely combines network and endpoint visibility, threat detection, and AI-powered analysis for faster, more effective incident response. Customers rely on us to minimize risk and complexity while maximizing operational resilience. www.nozominetworks.com 

View original content to download multimedia:https://www.prnewswire.com/news-releases/nozomi-networks-lands-co-development-project-with-lockheed-martin-to-strengthen-cybersecurity-for-government-and-defense-environments-302939296.html

SOURCE Nozomi Networks

Continue Reading

Technology

Europe records the world’s highest deepfake fraud rate as AI agents and cross-border networks rise

Published

on

By

Fraud attempts have fallen 28% worldwide but attacks are more complex in every region, Sumsub finds in its annual Identity Fraud Report

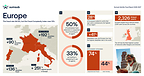
LONDON, Nov. 17, 2026 /PRNewswire/ — Sumsub, the first AI-powered trust infrastructure, has released its annual Identity Fraud Report 2026-2027, revealing that Europe now has the highest detected deepfake rate in the world at a rise of 41%, the sharpest increase of any region.

Globally, fraud is falling in volume but becoming harder to stop as fraudsters band together to create complex, AI-assisted schemes that easily outpace modern detection standards. The report finds that global fraud rates fell by 28% in 2026, but deepfake fraud rates nonetheless increased by 31% worldwide.

This has led Sumsub to the creation of the Fraud Complexity Index* (FCI), which scores each confirmed case on the tooling, coordination and number of techniques behind it. In its first year, the index finds that fraud complexity rose from 2.1 to 2.2 globally, indicating that fraud is concentrating, combining more techniques, automation and people. This is most evident in Europe, where fraud fell 8% while complexity rose by 13%.

Key findings

While global fraud may be falling in volume, it is becoming harder to detect, more coordinated and further reaching.

Nearly three in four (74%) European consumers experienced fraud in the past year. Of those, 44% lost money, and 38% of those recovered nothing.65% of European businesses reported confirmed or suspected fraud.Over half (53%) of businesses worldwide detected or suspected fraud involving an AI agent, yet only 37% could verify who authorised an agent to act.A third of global businesses hit by fraud say at least a quarter of their cases were linked to a wider fraud network, but only 21% use network analysis to detect these links.The UK hosts Europe’s third-highest number of organised fraud networks, despite UK fraud rates falling 40%, pointing to fewer but more coordinated groupsOver a quarter (28%) of Europeans asked to verify their age online used a workaround, the highest of any region. Over one in ten (13%) were wrongly rejected, and a further 13% abandoned the check.Fraud rate freefall may give platforms a false sense of security: Complex fraud is rising in online media (30%), e-commerce (19%) and crypto (16%). 

Fraud networks are spreading across borders

Globally, around one in 50 people who pass verification are later linked to a detected fraud network, as accounts are sold, taken over or opened on a fraudster’s behalf. Fraud networks are groups of orchestrated accounts linked by shared devices, identities, payment details, and documents. They buy, hack or coercively take accounts from legitimate people to pass checks without any apparent wrongdoing.

Europe’s largest detected network linked 2,326 such users across 28 countries. The UK recorded the third-highest number of detected networks in the region, after Bulgaria and Ukraine. The UK’s Fraud Strategy states more than two-thirds of fraud cases have an international element, making it difficult for businesses or regulators to detect them or understand the size of the operation.

Fraudsters dismiss underused AI defences with AI fakes

AI-generated deepfake fraud increased in over three quarters of markets analysed, with Italy seeing the sharpest rise at a 251% increase. The relationship between overall fraud volume and deepfakes was clearest in regions where fraud fell: Switzerland (fraud down 30%, deepfakes up 192%) and Portugal (down 18%, up 136%).

European defences haven’t kept pace. European businesses name AI-generated documents – which now make up 5% of all confirmed fraud – as the main reason fraud is harder to detect with current automated processes, yet document checks still remain their most common control. 

Just 26% of European businesses use biometric or liveness verification, less than a quarter use device intelligence (23%), and only 16% use network analysis. Under one in five run fraud data, tools and casework in a single system (19%), so the signals that would expose a complex fraud attempt remain siloed.

AI agents: cautious adoption yet wide exposure

Despite over half of European businesses reporting they detected or suspected fraud involving an AI agent this year, just 27% of European businesses verify who authorises an agent, and most worryingly, only 10% can suspend or revoke its access.

Globally, 49% of all agentic fraud incidents involved a legitimate agent manipulated by malicious instructions, and in 30% the agent made a purchase, payment or transfer.

Europe is slower than most to adopt with only 27% using agents internally this year, but such agents give fraudsters express access to the most sensitive and volatile business systems. Fewer than one in four businesses worldwide log what their agents do, so most wouldn’t know of such an incident before it’s too late.

This summer saw several high-profile incidents of AI models going beyond their intended limits. Meta saw its agentic account recovery process for Instagram hacked, affecting up to 20,000 accounts, shortly after an OpenAI model broke out of its test environment to hack the AI platform Hugging Face. Without intervention, we should expect to see cases like this accelerate as agentic processes become more common in the workplace.

Age checks remain unpopular and unprepared for upcoming regulation

62% of parents and guardians surveyed say a child in their care experienced online harm in the past 12 months, most often because of impersonation (28%). 

Support for age checks is lowest in Europe (68%), compared to 74% of global respondents, and only 9% of consumers worldwide said a check made a service feel safer. After a failed or intrusive check, 17% of consumers switched to another service, and 13% went looking for one without checks.

In the UK, the Online Safety Act has required highly effective age checks since July 2025, and this will soon apply broadly across Europe following the EU KIDS Act.

Regulators are looking for ways to make checks less intrusive. The EU’s European Digital Identity Framework states that members must offer a European Digital Identity Wallet by 24 December 2026. Wallets let a user prove they are over 18 without handing over their full identity; Sumsub found that 31% of consumers would adopt it for this reason. But with only 27% of European consumers having used a government digital ID wallet, and most member states not expected to meet the December deadline, platforms can’t afford to rely on any single solution to meet demand.

“What gives me confidence about Europe is that the direction of travel is becoming much clearer,” said Jacob Thompson, VP of Sales at Sumsub. “Regulation is still complex, but we’re moving toward more harmonised rules around payments, identity and financial crime, rather than every market solving the same problem differently. Fraudsters will obviously keep adapting, but over time that should make it easier for businesses to build controls that work consistently across borders instead of patching together a different approach country by country.”

To read the full Identity Fraud Report 2026-2027, visit: https://sumsub.com/identity-fraud-report-2026/

About Sumsub

Sumsub is the first AI-powered trust infrastructure for compliance operations at scale. By bringing together identity and business verification, fraud prevention, ongoing monitoring, and risk management in a single layer, Sumsub enables companies to streamline operations, adapt to evolving regulations, enter new markets, and grow securely.

Recognised as a Leader by Gartner, Forrester, and IDC, Sumsub combines seamless integration with advanced fraud prevention to deliver industry-leading performance. Sumsub also invests in responsible AI innovation through its AI Academic Program, forming alliances with top academia and institutions globally to enhance the world’s resilience against AI-powered fraud.

Methodology

Sumsub’s Identity Fraud Report 2026-2027 compares internal identity verification and user activity data from 2025 and 2026. In some cases, it includes data from 2021 to 2024 to show longer-term trends. It covers 5.8 million fraud samples and includes only jurisdictions with more than 15,000 verification attempts in the reporting period. The data has been aggregated and anonymised, and all graphs and infographics are based on the data of consenting customers.

Sumsub conducted its Fraud Exposure Survey in August 2026. It gathered responses from more than 1,400 fraud and risk professionals and more than 1,500 consumers in 21 markets across North America, Latin America, Europe, Asia, Africa and the Middle East.

*About the Fraud Complexity Index (FCI): The Fraud Complexity Index measures the technical and operational complexity of the average fraud case. Each recorded case is scored according to the types of distinct techniques used, from traditional forgery to fake liveness simulation. Attacks using more tooling, automation and coordination score higher, as do cases involving combinations of distinct techniques.

View original content to download multimedia:https://www.prnewswire.co.uk/news-releases/europe-records-the-worlds-highest-deepfake-fraud-rate-as-ai-agents-and-cross-border-networks-rise-302941828.html

Continue Reading

Technology

More Than Half of Organizations Using AI Agents Run Them Across Multiple Platforms, Nudge Security Research Finds

Published

on

By

Second edition of “AI Adoption in Practice” report shows AI risk now lives on the Workforce Edge, where employees choose, connect, and use technology, as agents and AI integrations reach company data outside traditional security controls

AUSTIN, Texas, Nov. 17, 2026 /PRNewswire/ — Nudge Security, the leading innovator in SaaS and AI security governance, today announced its research report, AI Adoption in Practice 2026: Beyond the Approved List, which provides insights into what AI adoption in the workforce looks like in practice. Based on anonymized and aggregated telemetry from Nudge Security customer environments, the report found that AI agents are already running inside the business platforms employees use every day, and that AI tools connect directly to company data in ways traditional security controls don’t see.

“The platforms your teams use every day are becoming agent platforms, whether or not anyone decided they should be. The project tracker, the CRM, the chat tool: each one now lets an employee build something that acts on their behalf, with their access, continuously. The question for security teams is no longer whether that’s allowed. It’s whether they know it’s happening,” says Nudge Security Cofounder and CTO Jaime Blasco. “We expect this to get harder, not easier. Every platform your teams use is adding agent-building features, and each one makes it simpler to hand an agent a person’s access. That means the gap between what an organization’s identity provider knows about and what’s actually acting on its data is going to keep widening.”

Key findings include:

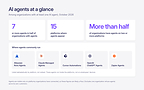
Many agents run on employees’ identities. Among organizations using AI agents, half run seven or more, and more than 4 in 10 run more than 10. They’re spread across business platforms like project management, CRM, and automation tools. Agents built inside these platforms often act through the employee who created them, with that person’s access to company data.AI connects directly to the most sensitive systems. 74% of organizations have at least one Anthropic integration and 67% have an OpenAI integration. These reach email, code, chat, and documents, and they move data without passing any inspection point.Core AI models are treated like a commodity. At least 91% of organizations have both OpenAI and Anthropic. Anthropic’s adoption rose from 77.8% in January to 94.5%.AI adoption extends well beyond the big two. Twelve different AI tools now each appear in more than half of organizations, up from five in January. Counting every AI tool in each environment, half of organizations have had 27 or more show up as of October 2026.AI in the browser sees what employees see. Among organizations with at least one AI browser extension, 67% have Grammarly and 65% have Claude. Both can read the content of the pages employees open.Company data flows into AI as part of everyday work. 18% of observed prompts include pasted content or an uploaded file, compared with 17% in the first report. Prompts are also reaching more AI tools: OpenAI still receives more than half of all observed prompts, but its share fell from 67% to 55% as more prompts go to other tools.

The report is based on anonymized and aggregated telemetry collected across Nudge Security customer environments. Rather than relying on surveys or self-reported usage, it reflects direct observation of AI tools, integrations, browser extensions, agents, and how employees interact with AI. Adoption, integration, and browser extension data is as of September 2026, and agent data is as of October 2026. The dataset includes organizations in Nudge Security’s first report, AI Adoption in Practice: What Enterprise Usage Data Reveals About Risk and Governance, as well as customers who have joined since.

What Security Leaders Can Do Now
Visibility alone will not reduce AI risk, so the report recommends focusing on where exposure is actually growing.

First, inventory agents where they are built in the business platforms teams already use, and identify who created each one and whose access it runs on.Second, treat OAuth grants as a first-class risk by reviewing which AI tools employees have connected to, what each grant can read, and revoking any that are no longer needed.Third, stop relying on the approved list as the main control and shift attention from which tools are present to what they are connected to.Fourth, review AI browser extensions that can read page content and set clear expectations for which are appropriate for sensitive work.Fifth and final, bring the workforce into the decision. Employees often know why they connected a tool, so ask, guide, and reserve the strictest response for the decisions that carry the most risk.

Download the full report: https://www.nudgesecurity.com/content/ai-adoption-in-practice-nov-2026.

About Nudge Security
Nudge Security is the AI and SaaS security platform for the Workforce Edge. Every day, employees sign up for apps, connect AI tools, and grant access to company data on their own. Together, those decisions create the Workforce Edge: an attack surface security teams own, even when they can’t see it. Nudge finds those apps, accounts, and connections from the first signup and prioritizes them by risk, with AI agents taking repetitive review work off the team’s plate. Then it goes straight to the employee behind the decision—to ask why, guide the next step, or fix the issue—and steps in directly when the risk is real. Security and IT teams govern the workforce’s technology without blocking productivity. Nudge Security was founded in 2021 by Russell Spitler and Jaime Blasco and is backed by Ballistic Ventures, Forgepoint Capital, Cerberus Ventures, and Squadra Ventures.

Media Contact:
Danielle Ostrovsky
Hi-Touch PR
Ostrovsky@Hi-TouchPR.com

View original content to download multimedia:https://www.prnewswire.com/news-releases/more-than-half-of-organizations-using-ai-agents-run-them-across-multiple-platforms-nudge-security-research-finds-302940529.html

SOURCE Nudge Security

Continue Reading

Trending