Connect with us

Technology

Britive ARC™ Brings Zero Standing Access to the AI Workforce

Published

on

Agentic Runtime Control gives AI agents intent-bound, task-scoped access only when work requires it, controls what they can do at runtime, and removes access when the task is complete 

LOS ANGELES, Aug. 24, 2026 /PRNewswire/ — Britive, the platform making standing privilege obsolete for agentic AI, non-human, and human identities, today introduced Britive ARC™ (Agentic Runtime Control), a new approach to securing AI agents as they move from assistants that answer questions to virtual workers that take action inside enterprise systems. 

Enterprises are building a new kind of workforce. Alongside teams of people, employees increasingly have virtual teams of AI agents that query databases, call APIs, change infrastructure, and act on problems surfaced by other agents. Britive ARC™ was shaped around the real-world requirements of enterprise customers already working through how to securely move AI agents into production. Like human workers, those agents need authority to perform different jobs. Unlike human workers, they should not need privileged access sitting idle between tasks. 

That creates a fundamental question: How do you give an AI agent enough authority to do its job without giving it privilege it can keep, misuse, or expose? 

Britive ARC™ answers that question by tying access to the work being performed. Each access grant is evaluated in context, including the identity behind it, the task, and the scope required. When authorized, Britive provides only the access needed, controls how it can be used while the work runs, and removes it when the task is complete. 

“One of the biggest barriers to moving agentic AI into production is knowing how to secure it,” said Chris Rasco, Head of AI/ML Platforms, Atlanta-based Financial Services Company. “Britive’s approach addresses a foundational part of that problem: giving agents only the access they need for the task, when they need it, without leaving standing access behind. Bringing agent access into the same platform used to manage human and non-human access provides the kind of foundation enterprises need to move from experimentation into production with confidence.” 

A new access model for a new workforce 

Traditional access models were built around people and predictable machine identities. AI agents are different: they perform specific tasks on behalf of people, services, or other agents, at machine speed. Standing privilege was risky for humans. For autonomous agents, it’s reckless. 

Britive ARC™ controls the critical security moments of an agent transaction through a continuous model: verify, assess, authorize, observe, and revoke.  

Britive verifies the agent and the identity it acts for where applicable, evaluates the intent and the prompt context, provides only the required access, observes the activity while it runs, and removes access when it is no longer authorized or needed. 

Throughout the transaction, Britive captures evidence of the identities, requests, authorization decisions, privileges, actions, and outcomes involved. For agent tool calls, that can include the prompt, tool, arguments, and, where supplied, the agent’s stated intent. 

“Most of the industry is focused on how to protect the credential an AI agent holds. We think that starts with the wrong assumption,” said Art Poghosyan, CEO and co-founder of Britive. “The better question is why an agent should have privileged access to keep at all. Britive ARC™ ties privilege to the work being authorized. It can appear when the task requires it, remain under control while the work happens, and disappear when the work is done.” 

Privilege is temporary. Control is continuous. Proof is captured throughout. 

Zero standing privilege, with control after access 

Britive ARC™ can elevate an agent’s permissions directly inside the target system without issuing the agent a privileged credential to hold. For systems that require credentials, Britive can create and inject them at runtime and revoke them when the task ends. 

“Every AI agent is another identity with access to your most critical systems and data. If we wouldn’t accept standing privileges for our engineers, we shouldn’t accept them for agents,” said Chetan Jha, Head of Identity and Data Security at Marqeta. “What’s compelling about Britive ARC™ is that access can be created for the task, scoped to what the agent actually needs, and removed when the work is done.” 

Control also continues after access is granted. Through the Britive MCP Gateway, agent tool calls are evaluated against centralized policy at runtime before unauthorized actions are executed on downstream systems. Where Britive sits in the connection path to the resource, enforcement can extend to individual SSH commands and SQL statements. An agent authorized to read from a database, for example, can still be stopped from performing an unauthorized destructive action. 

Authorization can also change while work is underway. Shared Signals Framework events, including CAEP and RISC signals, can trigger additional enforcement or revoke active session as conditions change. 

One platform for the people and agents doing the work 

AI agents act for people, interact with machine identities, and reach systems already governed by enterprise access policies. Britive ARC™ brings agentic AI into the same runtime policy and access enforcement platform used for human and non-human identities across hybrid, multi-cloud, SaaS, database, server, and on-premises environments. 

When an agent acts on behalf of a person, Britive can keep the agent’s authority at or below that person’s authority and narrow it further to the privileges permitted for that agent, for a specific task, resource, or content. The delegating identity and the agent remain connected throughout the transaction and audit record. 

That same modern, runtime-first architecture is also reflected in Britive’s selection by AWS for inclusion in AWS Security Hub Extended, reinforcing Britive’s Zero Standing Privileges approach and the architecture behind Britive ARC™. 

Availability 

Britive ARC™ is available today on the Britive platform, with capabilities spanning AI agent discovery and governance, runtime tool-call authorization through the Britive MCP Gateway, runtime elevation, access enforcement, on-behalf-of delegation, and signal-driven revocation.

Learn more about the feature and additional resources at http://britive.com/resource/blog/britive-arc-securing-ai-agents-beyond-mcp-gateway 

About Britive 

Britive is the runtime authorization platform for every identity that runs the modern enterprise: AI agents, non-human identities, and people. Instead of managing standing accounts and long-lived credentials, Britive creates privilege at the moment an authorized action requires it and removes it when the work is done, across clouds, SaaS applications, databases, servers, and systems that still depend on traditional credentials. One policy model, one audit trail, and one platform govern every identity type, with no endpoint software to deploy.  

With Britive ARC™, Agentic Runtime Control, the same standard now extends to AI agents: access checked out for the task, enforced down to the individual command, and gone when the task ends. Nothing is left standing. Learn more at britive.com

Media Contact 

Miad Moussawi 

miad.moussawi@britive.com

View original content to download multimedia:https://www.prnewswire.com/news-releases/britive-arc-brings-zero-standing-access-to-the-ai-workforce-302857786.html

SOURCE Britive

Continue Reading

Technology

NatGold Digital Announces Immediate Delisting of NATG from MEXC Following U.S. Treasury Action

Published

on

By

CORAL GABLES, Fla., Nov. 7, 2026 /PRNewswire/ — NatGold Digital Ltd. (“NatGold” or the “Company”) today announced that it has requested the delisting of the NatGold Token (NATG) from MEXC, a global cryptocurrency exchange where NATG is currently listed, with immediate effect.

The decision follows the U.S. Department of the Treasury’s announcement of an order issued by its Financial Crimes Enforcement Network (FinCEN) under the Combating Russian Money Laundering Act, prohibiting U.S. financial institutions from processing funds transfers involving MEXC Global.

NatGold is a U.S. company whose wholly owned subsidiary, NatGold Integrity Vault LLC, is registered with FinCEN as a money services business. The Company is acting ahead of the order’s effective date.

“As a U.S. company operating through a FinCEN-registered money services business, we are acting immediately in response to Treasury’s decision,” said Mark Radke, Executive Chairman of NatGold Digital. “Trust is a cornerstone of NatGold’s operating structure, and responding promptly to this regulatory action reflects that commitment.”

NatGold is in advanced discussions with multiple regulatory-compliant exchanges and venues  serving global markets, including the United States, and intends to replace MEXC as soon as possible. Once new listings are confirmed, NATG token holders will be advised of the arrangements and encouraged to register accounts and link their wallets, as applicable, to continue trading.

About NatGold Digital Ltd.

NatGold Digital Ltd. is the global leader in digital gold mining and the architect and operator of a patent-pending, non-extractive platform designed to unlock the intrinsic value of technically verified in-ground gold resources that remain securely stored in Mother Nature’s Vault. NatGold Tokens are structured to represent standardized unit interests in NatGold Certified Resources, disclosed under internationally recognized geological Technical Reports — without physical extraction, processing, or movement of gold. The result is a superior fiat money alternative designed to help lead a global monetary reformation.

For additional background, please visit NatGold.com or our official YouTube channel for videos and information about our digital mining ecosystem: youtube.com/@NatGold_Digital.

Contact

Media@NatGold.com
InvestorServices@NatGold.com
+1 (646) 825-3038

The information in the above release has been prepared by NatGold Digital Ltd. (“NatGold”) using its best efforts to realistically and factually present the information contained herein. However, subjective opinion, reliance on factors outside NatGold’s control, and external information sources unavoidably mean that NatGold cannot warrant the information to be exhaustive, complete, or sufficient. The information provided herein is intended solely for general informational purposes and does not constitute an offer or solicitation for the purchase or sale of any shares or securities of NatGold or for the purchase or sale of any NatGold Tokens. NatGold Tokens are not intended to be “securities” in any jurisdiction, and NatGold makes no claim or representation related to the value of NatGold or NatGold Tokens. Potential investors should seek advice from a qualified financial dealer before investing in NatGold. There are substantial risks associated with investing in development-stage digital assets and technology companies.

View original content to download multimedia:https://www.prnewswire.com/news-releases/natgold-digital-announces-immediate-delisting-of-natg-from-mexc-following-us-treasury-action-302932601.html

SOURCE NatGold Digital Ltd.

Continue Reading

Technology

What to Look for in an Online GLP-1 Provider: Meant Outlines Five Questions Worth Asking Before Signing Up

Published

on

By

MANASSAS, Va., Nov. 7, 2026 /PRNewswire/ — As more telehealth companies offer GLP-1 care, the options can look alike from the outside, and telling them apart takes more than a glance at a landing page. Meant is sharing five questions consumers can ask when choosing an online GLP-1 provider, along with how it approaches each one.

Five Questions Worth Asking

Who makes the clinical decisions? A trustworthy provider should be clear about which licensed clinicians review each person’s information. At Meant, those decisions are made by licensed providers through its clinical partner, OpenLoop Health.Is there a real evaluation first? Look for a health-history review before anything is prescribed, and for plain language that a prescription is never guaranteed. Meant’s online assessment covers health history, current medications, and goals.Can the company’s credentials be checked? Independent certifications are one signal consumers can verify for themselves. Meant displays the seal for its LegitScript certification on its website.Is it clear who fills prescriptions? Providers should be open about the pharmacies they work with and whether those pharmacies are licensed in the United States.Is ongoing support spelled out, limits included? Good providers explain what follow-up looks like and who handles which questions. Meant pairs care with an optional Care Coach, and medical questions go to the care team.

A certification is a transparency signal, not a government approval or a promise about results, and no checklist replaces a conversation with a licensed clinician. Meant does not diagnose or prescribe, and treatment is not guaranteed for every applicant.

Take a Closer Look

Consumers who want to see how the assessment, clinical oversight, and coaching fit together can visit Meant‘s website and compare the details against the questions above.

About Meant

Meant is a health and wellness technology company focused on personalized GLP-1 weight-care support delivered through telehealth. The platform combines an online clinical assessment, licensed oversight through OpenLoop Health, Care Coach support, and supplemental wellness resources. Meant does not itself diagnose or prescribe; clinical decisions are made by its clinical partners. Learn more at meant.health.

Meant Health, Inc.
support@meant.health
1-512-879-9187
10199 Dean Drive, Manassas, VA 20110, USA

View original content:https://www.prnewswire.com/news-releases/what-to-look-for-in-an-online-glp-1-provider-meant-outlines-five-questions-worth-asking-before-signing-up-302927805.html

SOURCE Meant

Continue Reading

Technology

Capturing the Beauty of Anhui through Images–2026 Anhui Photography Season Concludes

Published

on

By

HUANGSHAN, China, Nov. 7, 2026 /PRNewswire/ — A news report from Crionline.

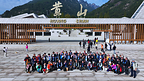
Spanning summer and autumn across three successive photography tours, the “Picturesque Anhui • Imaging Anhui” 2026 Anhui Photography Season officially wrapped up on November 4. Co-hosted by the Fédération Internationale de l’Art Photographique (FIAP), the Anhui Provincial Department of Culture and Tourism, and the Foreign Affairs Office of Anhui Provincial People’s Government, the event drew 116 photographers from 38 countries and regions. They visited 46 distinctive cultural and tourism attractions across five cities: Hefei, Chizhou, Anqing, Huangshan and Xuancheng. Through their lenses, they presented Anhui’s landscapes, cultural heritage and vibrant everyday life to the world.

Looking back on the three sessions: The first session kicked off in Hefei. Photographers documented the city’s innovation-driven urban landscape as well as the picturesque scenery and intangible cultural heritage of Chizhou’s ancient villages. The second session took them deep into Huangshan and Anqing. They explored time-honored Huizhou villages, magnificent mountains and Huangmei Opera culture, immersing themselves in Huizhou traditions and the cultural charm of the Yangtze River region in western Anhui. The concluding third session was held in Huangshan and Xuancheng, focusing on brilliant autumn hues, Huizhou‑style ancient architecture, and the traditional craftsmanship behind the Four Treasures of the Study.

From lush summer greens to rich autumn colours, the photographers produced more than 11,000 high‑resolution photographs. Reflecting the unique perspectives of international participants, these images will be disseminated globally in diverse forms. They will help tell compelling stories of Anhui’s cultural tourism and further boost the province’s international profile.

View original content to download multimedia:https://www.prnewswire.com/apac/news-releases/capturing-the-beauty-of-anhui-through-images2026-anhui-photography-season-concludes-302932583.html

SOURCE Crionline

Continue Reading

Trending