Connect with us

Technology

LRQA and K-Frontiers strengthen local inspection capabilities in Malaysia through strategic partnership

Published

on

KUALA LUMPUR, Malaysia, Oct. 15, 2026 /PRNewswire/ — LRQA, a leading global assurance partner, has strengthened its presence in Malaysia through a strategic partnership with K-Frontiers Sdn Bhd, an established Malaysian service provider to the oil and gas industry.

Following completion of the transaction, K-Frontiers has acquired a 51% stake in LRQA Inspection Malaysia Sdn Bhd, becoming LRQA’s local partner in Malaysia. The partnership will strengthen LRQA’s ability to provide inspection and assurance services to customers across Malaysia’s energy and industrial sectors.

Malaysia’s oil and gas sector continues to play an important role in the country’s economy and regional energy landscape. As projects and supply chains become increasingly complex, the partnership will support customers with relevant inspection capabilities and assurance services.

Kit Wong, Business Director SEA, LRQA, said:

“We are delighted to partner with K-Frontiers, an organization that shares our commitment to trust, professionalism, and long-term value creation. This partnership marks an important step in strengthening our combined capabilities and delivering greater value to customers across the region. By bringing together our complementary expertise, local knowledge, and shared commitment to operational excellence, we are well positioned to address evolving industry needs and pursue new opportunities. We look forward to building a successful and sustainable relationship that creates lasting value for our customers and stakeholders.”

Osart Jallong, Founder & Managing Director, K-Frontiers Sdn Bhd, said:

“We are pleased to enter this partnership with LRQA, bringing together its global expertise and assurance capabilities with K-Frontiers’ industry experience and strong local presence. Our organizations share a commitment to quality, integrity, and customer success, providing a solid foundation for collaboration. We believe this partnership will enable us to offer enhanced solutions, respond more effectively to our customers’ evolving needs, and create sustainable value for the energy sector across the region.”

The partnership forms part of LRQA’s broader strategy to strengthen its presence and capabilities across key markets in Asia Pacific and support customers as they navigate increasingly complex technical and operational challenges.

About LRQA

From certification and cybersecurity to safety, sustainability and supply chain resilience, LRQA works with clients to identify risks across their business. We design smart, scalable solutions, built around your business – tailored to help you prepare, prevent and protect against risk. Our innovative risk management portfolio helps shape a stronger and more secure future for your business. With decades of sector-specific expertise, data-driven insight and on-the-ground teams across assurance, certification, inspection, advisory and training, we support over 61,000 clients in more than 150 countries. For more information, visit https://www.lrqa.com/

About K-Frontiers

K-Frontiers Sdn. Bhd. is a Malaysian oil and gas services company established in 2002 and headquartered in Miri, Sarawak. It provides well engineering consultancy, drilling and completion support, field services, pressure-testing solutions, and skilled technical manpower. The company supports leading energy operators by combining industry expertise with strong local knowledge and dependable operational delivery. Guided by the values of care, trust, integrity, and professionalism, K-Frontiers aims to be a long-term “Partner of Choice” for its clients, employees, and stakeholders. For more information, visit https://www.kfrontiers.com/

Further information
For more information, please contact:

Hasan Surve 
Regional Marketing Manager – APAC, LRQA 
hasan.surve@lrqa.com


View original content to download multimedia:https://www.prnewswire.co.uk/news-releases/lrqa-and-k-frontiers-strengthen-local-inspection-capabilities-in-malaysia-through-strategic-partnership-302909840.html

Continue Reading

Technology

CSL Group Acquires SIMPL Wireless to Bring Critical Connectivity® to North America

Published

on

By

Adding multi-carrier eSIM, a unified connectivity management platform and Tier-1 US carrier partnerships to CSL’s global IoT connectivity platform

LONDON and DULUTH, Ga., Oct. 16, 2026 /PRNewswire/ — CSL Group, the leading global provider of Critical Connectivity®, has acquired SIMPL Wireless, the US-based IoT eSIM connectivity provider. The acquisition gives CSL a North American home and gives customers connectivity that is simple, fast and fully under their control, within a single, resilient connectivity service.

As IoT estates grow across borders, enterprises need to manage every SIM, contract and network from one place. Unified management lowers cost and speeds deployment, while multi-network resilience keeps devices connected when a network goes down.

The acquisition, CSL’s second in 2026 following IoTM Solutions in July, strengthens CSL’s ability to help customers build resilient IoT estates – with the uptime and operational control that life, mission and business-critical applications demand.

Simple. Fast. Yours.

SIMPL’s promise is simple, fast and yours: connectivity that goes live quickly, runs on the SIMs, APNs, hardware and carrier contracts customers already have, and keeps them in control of every connection. EverSIM, its multi-carrier eSIM built on unmodified, GSMA SAS-certified Thales eUICC infrastructure and native to SGP.22 and SGP.32, gives customers the option to buy connectivity from SIMPL or bring their own from up to 100 mobile network operators, with 5G Standalone support, backward-compatible to NB-IoT. A single SIM SKU carries a native primary carrier profile, and customers can localise anywhere by downloading local profiles over the air, with backup profiles that step in automatically if the primary network goes down and hand back when it returns. Compass, its single-pane-of-glass platform, gives customers one dashboard and one API to activate, monitor and manage SIMPL SIMs alongside existing carrier SIMs, with automated self-healing via auto-profile fallback.

Historically, enterprise eSIM deployments have taken a year or more because of platform integrations, carrier certifications and custom development. EverSIM compresses that timeline to days, enabling customers to move quickly from proof of concept to production while maintaining centralised oversight. Speed, simplicity, control – it just works.

With established partnerships including T-Mobile and Thales, SIMPL serves Solution Providers and Resellers in addition to customers across retail, transport, energy and EV charging.  This gives CSL an immediate US customer base, local go-to-market capability and Tier-1 carrier relationships.

Combined with CSL’s patented rSIM® multi-network resilience and IoTM’s connectivity orchestration, SIMPL completes a single operating model for customers: manage every SIM and eSIM, and stay online when a network fails.

Jason Morrow, CEO of SIMPL Wireless, said:

“SIMPL was built on three ideas: speed, simplicity and control. IoT connectivity should be fast to activate, run on what customers already have, and stay theirs to control – it should just work. Joining CSL Group puts that on a platform engineered for uptime and backed by three decades of critical connectivity expertise. For our customers, nothing changes on day one except what we can now offer them.”

The SIMPL team will join CSL Group, and SIMPL will continue to serve its existing customers, carriers and partners – as SIMPL Wireless, a CSL Group company.

Expanding CSL in North America

CSL already delivers managed IoT connectivity and patented rSIM® resilience across more than three million connections in building security, healthcare, infrastructure, utilities and transport. SIMPL gives CSL the US base, carrier relationships and local team to bring that capability to North American customers.

Together, CSL, IoTM and SIMPL enable customers to deploy globally, connect with confidence, automate SIM and eSIM lifecycle management and keep critical devices online as their estates grow.

Ed Heale, CEO of CSL Group, commented:

“Customers shouldn’t have to choose between flexibility and resilience. Bringing SIMPL into CSL Group gives us a home in North America and a platform that lets customers connect anywhere, with the certainty critical applications require.”

Financial terms of the transaction were not disclosed.

About CSL Group

CSL Group is the world’s leading provider of Critical Connectivity®. Founded in 1996, CSL has spent three decades building the expertise, resilience and managed infrastructure that life, mission and business-critical IoT applications depend on. Today, CSL manages over three million connections across building security, healthcare, infrastructure, utilities and transport, delivering always-on, fully managed, multi-path IoT solutions at scale. Where other connectivity providers deliver a commodity, CSL delivers certainty: designing, deploying and managing secure, resilient solutions tailored to the environments where failure is not an option.

Learn more at csl-group.com.

Follow CSL:

on LinkedIn

on Instagram

About SIMPL Wireless

SIMPL Wireless is a US-based eSIM-as-a-Service provider headquartered in Duluth, Georgia. Its EverSIM multi-carrier eSIM and Compass platform deliver IoT connectivity that is simple, fast and yours. Customers can buy connectivity from SIMPL or bring their own from up to 100 mobile network operators, activate quickly on the hardware and carrier contracts they already have, and manage every connection through one dashboard and one API. SIMPL is built on GSMA SAS-certified Thales infrastructure and works with partners including T-Mobile and Thales. SIMPL Wireless is a CSL Group company.

Learn more at justsimpl.com.

For more information, contact: marketing@csl-group.com

View original content to download multimedia:https://www.prnewswire.co.uk/news-releases/csl-group-acquires-simpl-wireless-to-bring-critical-connectivity-to-north-america-302910610.html

Continue Reading

Technology

Buck Institute President Dr. Eric Verdin Named Co-Chairman of Attilio

Published

on

By

Verdin, designer of the Dr. Verdin Baseline Assessment(TM), joins Attilio as Co-Chairman.

ST. PETERSBURG, Fla., Oct. 16, 2026 /PRNewswire/ — Attilio announced today that Dr. Eric Verdin, President and CEO of the Buck Institute for Research on Aging, has joined the company as Co-Chairman.

Verdin leads the Buck Institute, the first independent biomedical research institute in the world focused solely on aging and age related disease. Founded in Novato, California, the Institute helped build and legitimize the field now known as geroscience and has produced landmark discoveries in aging biology since its founding. Verdin has testified before the United States Congress on the science of aging and speaks widely on the subject, sharing findings directly with the public rather than keeping them inside academic journals.

As Co-Chairman, Verdin brings Attilio direct access to the research driving the field of geroscience, the biomarkers, imaging, and clinical protocols the Buck Institute uses to study aging in humans. He shapes the scientific direction behind every member’s care, drawing on decades spent identifying which interventions actually extend healthy life and which do not hold up to scrutiny. That same research underlies the Dr. Verdin Baseline Assessment(TM), which Attilio offers members for $2,500.

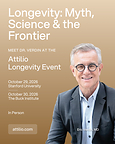
Verdin also headlines Attilio’s inaugural Longevity Event, October 29 and 30, 2026, at Stanford University and the Buck Institute for Research on Aging, alongside Dr. Laura Carstensen, Dr. Robert Waldinger of Harvard Medical School, and Dr. Dean Ornish.

“Eric is all in on this mission,” said Paul A. Pagnato, CEO & Founder of Attilio. “He brings decades of research and a direct line to the Buck Institute’s work. Now, as Co-Chairman, he helps shape where Attilio goes next.”

Attilio Mission: Democratize access to +100Year Quality Lifespan, reaching 99% of U.S. population.

Learn more about Attilio at www.attilio.com.

About Attilio

Attilio is a Human powered AI Life Optimization Platform(TM), technology, and Stewardship built to help people live longer, healthier lives. Every membership operates under the company’s Conflict-Free Standards(TM): no commissions, no revenue sharing, no self-dealing. Attilio launched in September 2026 under CEO & Founder Paul A. Pagnato, working with experts from Stanford University, Harvard University, and the Buck Institute for Research on Aging.

Media Contact
Lia Bliss, Chief Marketing Officer press@attilio.com https://attilio.com

View original content to download multimedia:https://www.prnewswire.com/news-releases/buck-institute-president-dr-eric-verdin-named-co-chairman-of-attilio-302910667.html

SOURCE Attilio One

Continue Reading

Technology

Keeper Security and Tenable Integrate to Streamline Cloud Risk Detection, Remediation and Vulnerability Assessment

Published

on

By

With new integrations, Keeper’s identity security platform remediates cloud security findings discovered by Tenable in seconds and secures the privileged credentials used for vulnerability scanning

CHICAGO, Oct. 16, 2026 /PRNewswire/ — Keeper Security, the leading zero-trust and zero-knowledge identity security platform, today announces native integrations with Tenable that eliminate the costly delay between identifying cloud security risks and remediating them while centralizing credential management for comprehensive vulnerability assessment. These integrations allow cloud security teams to move from detection to remediation in a single workflow, without managing manual tickets or switching between tools. Teams can now instantly act on Tenable’s findings to rotate compromised credentials, enforce Just-In-Time access and remove standing privileges, all without leaving the Keeper platform. Organizations can also eliminate static credentials from scan policies by storing privileged credentials centrally in Keeper, enabling Tenable to retrieve them automatically at scan time for credentialed scanning of SSH, Windows and database targets.

Tenable provides comprehensive visibility into exposed identities, risky access paths and misconfigurations across cloud environments. However, the gap between discovering these findings and executing remediation remains a persistent challenge for cloud security teams that typically manage this workflow manually across multiple tools. Teams can spend days or weeks chasing approvals and context-switching while risk persists in production, leaving the vulnerability window open for exploitation.

Keeper’s integration with Tenable closes this gap by sending cloud findings directly into Keeper’s remediation engine. Once a finding arrives in Keeper’s platform, security teams can immediately execute targeted fixes – including credential rotation, Just-In-Time (JIT) access enforcement and standing privilege removal – without leaving their existing workflow. When remediation is complete, Keeper automatically notifies Tenable and moves the finding to resolved status with zero manual follow-up. The entire cycle from detection to closure happens without teams switching platforms or managing tickets.

“Organizations can’t remediate findings if they aren’t properly equipped to take action immediately,” said Darren Guccione, CEO and Co-founder of Keeper Security. “As AI-powered threats increase the onslaught of cyber attacks and decrease the window of time in which cyber defenders can take action, this integration enables cloud security teams to implement fixes in seconds instead of weeks.”

Closed-Loop Remediation Without Exposure

The integration preserves Keeper’s zero-knowledge architecture at every step. Keeper Encrypter operates as a self-hosted gateway deployed inside the customer’s environment, receiving webhook traffic from Tenable and encrypting the data exchange using customer-managed private keys. All synchronization between platforms happens through encrypted channels that remain fully contained within the organization’s perimeter. Cloud infrastructure never sees unencrypted findings or credentials, and security teams achieve automated remediation without exposure.

The remediation workflow is straightforward and comprehensive. Teams send relevant Tenable findings directly to Keeper, then select the appropriate remediation action for each finding. For infrastructure compromises, teams can rotate exposed credentials across databases, machines, cloud environments and directories. For access control issues, they can enforce JIT access to eliminate standing privileges at scale. For cloud identities flagged by Tenable, teams can onboard PAM User records directly without requiring separate database, machine or directory resources. Each remediation action is logged with a full audit trail and compliance visibility.

“By connecting Tenable’s cloud detection directly to Keeper’s zero-trust remediation engine, we’ve built a closed-loop workflow that operates entirely within the customer’s perimeter,” said Craig Lurey, CTO and Co-founder of Keeper Security. “Security teams can immediately execute targeted fixes – from automated credential rotation to JIT access enforcement – without leaving their workflow or exposing unencrypted data.”

Centralized Credential Management for Credentialed Scans

Tenable’s integration with Keeper Commander solves another critical challenge: securing the credentials Tenable needs to log into systems during vulnerability scans. Today, organizations typically store passwords and SSH keys directly in Tenable scan policies, a practice that increases risk if either system is compromised. With this integration, organizations store those credentials securely in Keeper instead. When Tenable runs a scan and needs to log into a system, it requests the credential from Keeper, which delivers it securely, never allowing it to sit in Tenable’s configuration.

Credentialed scans allow the Tenable scanner to log in to target systems directly and perform deeper assessments than is possible without credentials, including checking installed software versions, configuration settings, patch levels and compliance status. This approach supports SSH, Windows (SMB) and database credentialed scans while keeping secrets out of scan policies. Credentials rotate in Keeper automatically, and Tenable picks up the new values at the next scan with zero manual policy updates.

For Teams Managing Cloud Risk at Scale

Both integrations are purpose-built for security operations teams managing cloud infrastructure at scale. Organizations can now detect cloud risks with Tenable, remediate them instantly through Keeper and run deeper vulnerability scans using centrally managed credentials without exposing secrets or switching between tools.

The Keeper Commander and Tenable integrations are available now to Keeper customers with active KeeperPAM licenses. To learn more about connecting Tenable findings to Keeper’s zero-trust remediation controls and securing credentials for authenticated scans, visit keepersecurity.com or schedule a demo with Keeper Security today.

About Keeper Security
Keeper Security is the leading zero-trust and zero-knowledge identity security solution, trusted by millions of people and thousands of organizations globally. KeeperPAM® is Keeper’s privileged access management platform that unifies password and passkey management, secrets management, privileged session management and endpoint privilege management in a single cloud-native platform, protected with quantum-resistant encryption. KeeperAI® delivers real-time, AI-native threat detection across every privileged session. As AI agents proliferate and identity becomes the defining attack surface, Keeper governs access for humans, machines, non-human identities and AI agents, serving as the unified control plane for access, compliance and visibility across the enterprise. For more information, visit KeeperSecurity.com.

Learn more: KeeperSecurity.com
Follow Keeper: Facebook Instagram LinkedIn X YouTube TikTok

Media Contact
Katherine Benfield
ICR for Keeper Security
KeeperSecurity@icrinc.com 

View original content to download multimedia:https://www.prnewswire.com/news-releases/keeper-security-and-tenable-integrate-to-streamline-cloud-risk-detection-remediation-and-vulnerability-assessment-302910900.html

SOURCE Keeper Security

Continue Reading

Trending