Connect with us

Technology

IBM Report: Ransomware Persisted Despite Improved Detection in 2022

Published

on

Manufacturing Most Extorted Industry; Email Thread Hijacking Attempts Spike; Time to Ransom Moves from Months to Days

ARMONK, N.Y., Feb. 22, 2023 /PRNewswire/ — IBM (NYSE: IBM) Security today released its annual X-Force Threat Intelligence Index finding that although ransomware’s share of incidents declined only slightly (4 percentage points) from 2021 to 2022, defenders were more successful detecting and preventing ransomware. Despite this, attackers continued to innovate with the report showing the average time to complete a ransomware attack dropped from 2 months down to less than 4 days. 

According to the 2023 report, the deployment of backdoors, which allow remote access to systems, emerged as the top action by attackers last year. About 67% of those backdoor cases related to ransomware attempts, where defenders were able to detect the backdoor before ransomware was deployed. The uptick in backdoor deployments can be partially attributed to their high market value. X-Force observed threat actors selling existing backdoor access for as much as $10,000, compared to stolen credit card data, which can sell for less than $10 today.

“The shift towards detection and response has allowed defenders to disrupt adversaries earlier in the attack chain – tempering ransomware’s progression in the short term,” said Charles Henderson, Head of IBM Security X-Force. “But it’s only a matter of time before today’s backdoor problem becomes tomorrow’s ransomware crisis. Attackers always find new ways to evade detection. Good defense is no longer enough. To break free from the never-ending rat race with attackers, businesses must drive a proactive, threat-driven security strategy.”

The IBM Security X-Force Threat Intelligence Index tracks new and existing trends and attack patterns – pulling from billions of datapoints from network and endpoint devices, incident response engagements and other sources.

Some of the key findings in the 2023 report include:

Extortion: Threat Actors Go-to Method. The most common impact from cyberattacks in 2022 was extortion, which was primarily achieved through ransomware or business email compromise attacks. Europe was the most targeted region for this method, representing 44% of extortion cases observed, as threat actors sought to exploit geopolitical tensions.Cybercriminals Weaponize Email Conversations. Thread hijacking saw a significant rise in 2022, with attackers using compromised email accounts to reply within ongoing conversations posing as the original participant. X-Force observed the rate of monthly attempts increase by 100% compared to 2021 data.Legacy Exploits Still Doing the Job. The proportion of known exploits relative to vulnerabilities declined 10 percentage points from 2018 to 2022, due to the fact that the number of vulnerabilities hit another record high in 2022. The findings indicate that legacy exploits enabled older malware infections such as WannaCry and Conficker to continue to exist and spread.

Extortion Pressure Applied (Unevenly)
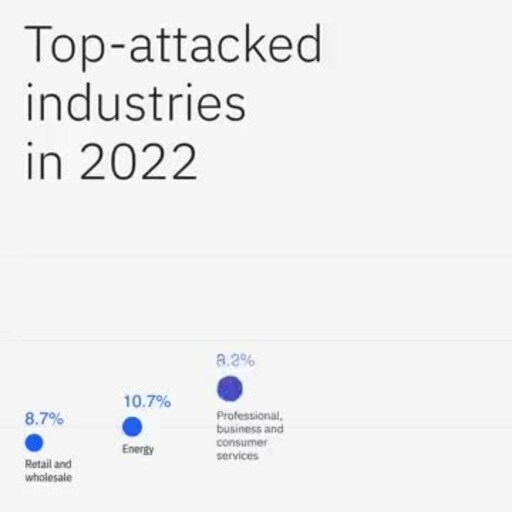
Cybercriminals often target the most vulnerable industries, businesses, and regions with extortion schemes, applying high psychological pressure to force victims to pay. Manufacturing was the most extorted industry in 2022, and it was the most attacked industry for the second consecutive year. Manufacturing organizations are an attractive target for extortion, given their extremely low tolerance for down time.

Ransomware is a well-known method of extortion, but threat actors are always exploring new ways to extort victims. One of the latest tactics involves making stolen data more accessible to downstream victims. By bringing customers and business partners into the mix, operators increase pressure on the breached organization. Threat actors will continue experimenting with downstream victim notifications to increase the potential costs and psychological impact of an intrusion – making it critical that businesses have a customized incident response plan that also considers the impact of an attack on downstream victims.

Thread Hijacking on the Rise
Email thread hijacking activity surged last year, with monthly attempts by threat actors doubling compared to 2021 data. Over the year, X-Force found that attackers used this tactic to deliver Emotet, Qakbot, and IcedID, malicious software that often results in ransomware infections.

With phishing being the leading cause of cyberattacks last year, and thread hijacking’s sharp rise, it’s clear that attackers are exploiting the trust placed in email. Businesses should make employees aware of thread hijacking to help reduce the risk of them falling victim.

Mind the Gap: Exploit “R&D” Lagging Vulnerabilities
The ratio of known exploits to vulnerabilities has been declining over the last few years, down 10 percentage points since 2018. Cybercriminals already have access to more than 78,000 known exploits, making it easier to exploit older, unpatched vulnerabilities. Even after 5 years, vulnerabilities leading to WannaCry infections remain a significant threat. X-Force recently reported an 800% increase in WannaCry ransomware traffic within MSS telemetry data since April 2022. The continued use of older exploits highlights the need for organizations to refine and mature vulnerability management programs, including better understanding their attack surface and risk-based prioritization of patches.

Additional findings from the 2023 report include:

Phishers “Give Up” on Credit Card Data. The number of cybercriminals targeting credit card information in phishing kits dropped 52% in one year, indicating that attackers are prioritizing personally identifiable information such as names, emails, and home addresses, which can be sold for a higher price on the dark web or used to conduct further operations.North America Felt Brunt of Energy Attacks. Energy held its spot as the 4th most attacked industry last year, as global forces continue to affect an already tumultuous global energy trade. North American energy organizations accounted for 46% of all energy attacks observed last year, a 25% increase from 2021 levels.Asia Tops the Target List. Accounting for nearly one-third of all attacks that X-Force responded to in 2022, Asia saw more cyberattacks than any other region. Manufacturing accounted for nearly half of all cases observed in Asia last year.

The report features data IBM collected globally in 2022 to deliver insightful information about the global threat landscape and inform the security community about the threats most relevant to their organizations. You can download a copy of the 2023 IBM Security X-Force Threat Intelligence Report here.

Additional sources

Read more about the report’s top findings in this IBM Security Intelligence blog.Sign up for the 2023 IBM Security X-Force Threat Intelligence Index webinar on Thursday, March 2, 2022, at 11:00 a.m. ET here.Schedule a consult with IBM Security X-Force.

About IBM Security
IBM Security helps secure the world’s largest enterprises and governments with an integrated portfolio of security products and services, infused with dynamic AI and automation capabilities. The portfolio, supported by world-renowned IBM Security X-Force® research, enables organizations to predict threats, protect data as it moves, and respond with speed and precision without holding back business innovation. worldwide security experts, IBM is trusted by thousands of organizations as their partner to assess, strategize, implement, and manage security transformations. IBM operates one of the world’s broadest security research, development, and delivery organizations, monitors 150 billion+ security events per day in more than 130 countries, and has been granted more than 10,000 security patents worldwide.

Press Contact:
IBM Security Communications
Michele Brancati
mbrancati@ibm.com


View original content to download multimedia:https://www.prnewswire.com/news-releases/ibm-report-ransomware-persisted-despite-improved-detection-in-2022-301752400.html

SOURCE IBM

Continue Reading

Technology

Trimble for Government Achieves ‘Initial Implementation’ Status for FedRAMP Class C (Moderate) Certification

Published

on

By

Milestone accelerates secure cloud adoption for federal, state and local entities managing infrastructure, spatial data and capital assets 

WESTMINSTER, Colo., Oct. 20, 2026 /PRNewswire/ — Trimble today announced that Trimble for Government is listed as ‘Initial Implementation’ status for Federal Risk and Authorization Management Program (FedRAMP®) Class C (Moderate) certification and is now listed on the FedRAMP Marketplace. In conjunction with seeking FedRAMP certification, Trimble is also pursuing GovRAMP authorization to support state, local and education (SLED) customers with reciprocal cybersecurity compliance standards.

This dual milestone marks a critical step forward in delivering a software as a service (SaaS) cloud environment built within a secure Government Community Cloud. Designed specifically for U.S. Federal Government departments, state and local agencies, and defense and civilian contractors, Trimble for Government provides a unified ecosystem for managing infrastructure, spatial data, capital projects, permitting and facility assets across their entire lifecycle.

Achieving FedRAMP Class C (Moderate) and GovRAMP alignment will enable public sector entities and Department of Defense (DoD) contractors to comply with stringent security mandates — including Cybersecurity Maturity Model Certification (CMMC) alignment — while modernizing digital engineering and asset management.

“Federal, state and local agencies face the dual challenge of modernizing critical infrastructure while maintaining uncompromising cybersecurity standards,” said Mark Schwartz, group president, AECO at Trimble. “Achieving ‘Initial Assessment’ status reflects our commitment to delivering mission-critical spatial, capital project and asset management capabilities inside a secure, audit-ready cloud boundary across all levels of government.”

Integrated cloud solutions built for government operations

The in-scope environment brings together Trimble’s proven field execution, asset, project and permitting software into four modular packages designed to support specific public sector outcomes:

Trimble® Field Collaboration: Delivers field data services using foundational spatial database infrastructure and GIS integration to support high-security field operations, map assets, and enable seamless field-to-cloud workflows across Trimble’s core Field Systems portfolio.Trimble Project Management powered by Trimble ProjectSight® software: Connects design-to-build workflows in the field, providing precision data layout, project tracking, collaboration and quality assurance across construction projects.Trimble Asset Management powered by Trimble Unity™ Maintain software: Serves as a centralized facilities data core for federal, state, and local government agencies, military installations, and public infrastructure — such as public buildings, utilities, and transportation networks — to optimize maintenance and long-term capital planning.Trimble Permit Management powered by Trimble Unity Permit software: Streamlines end-to-end management of permitting, licensing, land use and infrastructure rights-of-way in a fully compliant cloud environment.

The unifying in-scope element across all four packages is the Trimble Connect® platform, providing collaboration and a common data environment (CDE) across the Trimble for Government platform.

With assessment processes underway, Trimble continues to advance toward full FedRAMP and GovRAMP authorizations to ensure public sector customers can innovate with confidence.

About Trimble
Trimble is a global technology company that connects the physical and digital worlds, transforming the ways work gets done. With relentless innovation in precise positioning, modeling and data analytics, Trimble enables essential industries including construction, geospatial and transportation. Whether it’s helping customers build and maintain infrastructure, design and construct buildings, optimize global supply chains or map the world, Trimble is at the forefront, driving productivity and progress. For more information about Trimble, visit: www.trimble.com.

GTRMB

View original content to download multimedia:https://www.prnewswire.com/news-releases/trimble-for-government-achieves-initial-implementation-status-for-fedramp-class-c-moderate-certification-302913499.html

SOURCE Trimble

Continue Reading

Technology

Delta Development Team and The Good Drone Company Awarded U.S. Army Contract for Aerial Blood Delivery

Published

on

By

TUCSON, Ariz., Oct. 20, 2026 /PRNewswire/ — Delta Development Team (DDT), a leader in prehospital blood storage and cold chain technology, and The Good Drone Company (GDC) have been awarded a U.S. Army contract to develop a drone-based blood delivery capability for the Army Blood Link (ABL) program.

The program is part of the broader Armed Services Blood Program (ASBP), which supplies blood products to U.S. military forces worldwide. Army Blood Link is designed to support battlefield medical logistics through rapid, temperature-controlled delivery of lifesaving blood products to the field, providing an additional resupply option when traditional ground transportation is unavailable, delayed, or unsafe. Under the contract, The Good Drone Company will provide two U.S.-built prototypes of its hybrid vertical takeoff and landing (VTOL) cargo drone, each designed to transport up to six units of blood, while DDT will provide the temperature-controlled storage capability through its Delta ICE 2L Smart Blood Cooler.

The companies are combining commercial off-the-shelf (COTS) technologies to create a U.S.-sourced aerial blood delivery system capable of transporting blood directly to the point of need.

To meet ABL program requirements, DDT will supply six Delta ICE 2L Smart Blood Coolers, each designed to maintain two units of blood within the required temperature range for three hours of aerial delivery in high-humidity environments with ambient temperatures ranging from 15°F to 120°F. Built-in temperature monitoring and data recording, along with Bluetooth and cellular connectivity, support cold-chain oversight and blood accountability. The program extends DDT’s blood storage and monitoring capabilities into aerial delivery.

“Getting blood to the point of need is only part of the challenge. It must also remain within the required temperature range throughout the journey,” said Montgomery Leija, CEO of Delta Development Team. “This program brings DDT’s experience in blood storage and cold chain management into a new operational environment, taking the blood supply chain from the ground to the air.”

The prototype system is designed to deliver blood within 10 meters of a designated target during both day and night operations. It will feature a communications range of up to 30 miles and semi-autonomous waypoint navigation. It is intended for single-person operation with minimal training and is built on GDC’s existing commercial cargo drone technology to accelerate development and fielding while meeting U.S.-sourcing requirements.

“We have seen strong interest in middle-mile drones in emerging markets for some time, from both public and private sector customers spanning healthcare to third-party logistics,” said Jake Vander Ploeg, CEO of The Good Drone Company. “This program is a great example of how the military is adopting commercial technology like our cargo drones to quickly test new ideas in the field without starting a full aircraft development program.”

The collaboration combines GDC’s expertise in commercial drone platforms and aerial delivery with DDT’s temperature-controlled blood storage and transport capabilities to support:

Rapid resupply: Delivering blood when conventional ground transportation is unavailable or unsafe.Cold chain protection: Maintaining required blood temperatures during aerial transport.U.S.-sourced capability: Supporting domestic defense supply chain objectives.Accelerated development: Combining GDC’s existing commercial cargo drone technology with DDT’s established blood storage solutions.

The ABL effort addresses the challenge of delivering critical medical supplies in contested and austere environments. When terrain, damaged infrastructure, or tactical conditions prevent conventional resupply, aerial delivery combined with temperature-controlled storage can expand options for getting lifesaving blood products to service members when and where they are needed.

About Delta Development Team

Delta Development Team (DDT) is a U.S.-based medical technology company headquartered in Tucson, Arizona, specializing in blood storage, transport, monitoring, and logistics solutions for military and prehospital environments. DDT develops technology designed to keep blood available, traceable, and mission-ready from the blood bank to the point of injury. Its portfolio includes the APRU 6L, Delta ICE 2L, TBS 40L, and BloodCOMM® blood management platform.

Media Contact: info@deltadevteam.com | www.deltadevteam.com

About The Good Drone Company

The Good Drone Company (GDC) is an aerospace company headquartered in Tempe, Arizona, that designs and builds autonomous hybrid VTOL cargo drones for middle-mile logistics. GDC’s aircraft take off and land vertically without a runway, carry up to 55 lb (25 kg) of payload, and fly more than 300 miles (500 km) at speeds up to 93 mph (150 km/h). GDC is deploying in Kenya to close the middle-mile transportation gap for public and private sector customers, working closely with its local partner ThatcherX and the Kenyan government to change how goods move around the country.

Media Contact: info@thegooddronecompany.com | www.thegooddronecompany.com

View original content to download multimedia:https://www.prnewswire.com/news-releases/delta-development-team-and-the-good-drone-company-awarded-us-army-contract-for-aerial-blood-delivery-302913294.html

SOURCE Delta Development Team

Continue Reading

Trending