Connect with us

Technology

EY Pulse of the MedTech Industry Report 2026: Blockbuster performers and innovation drive record MedTech industry growth

Published

on

Broader MedTech industry at turning point, seeking positioning to optimize portfolios, differentiate technology and improve R&D

Innovation drives increased dealmaking and R&D investment: MedTech saw a resurgence in deal size with M&A value up 160% in the first half of 2026 vs. the same period in 2025, reflecting investments in next-generation technologies, including AI-enabled diagnostics, robotics, structural heart, diabetes care and minimally invasive therapies.AI is reshaping the future of value creation: AI integration in MedTech is unlocking new business opportunities and scalable value creation, alongside a record and growing number of FDA-authorized AI-enabled devices.Industry growth is expanding into alternative care settings: MedTech is increasingly moving beyond traditional care settings and capturing growth in alternative care markets, particularly the rapidly expanding ambulatory surgery center (ASC) market and direct to consumer/patient.

NEW YORK, Oct. 19, 2026 /PRNewswire/ — The 20th edition of the Ernst & Young LLP (EY US) Pulse of the MedTech Industry report finds that the global medical technology (MedTech) industry is at a turning point. Following a period of record-setting growth and investment across the US and Europe, the sector finds itself at a revenue high point, even amid challenges, including negative investor sentiment and persistent global trade and supply chain uncertainties.

20th edition: EY Pulse of the MedTech Industry Report: Blockbuster performers & innovation drive record MedTech growth

Despite a challenging operating environment, the MedTech industry saw sustained growth in 2025, reaching approximately US$650 billion in revenue and representing growth of 11%, and continued to demonstrate top-line performance in the first half of 2026, generating $325 billion in revenue, a 7.1% increase compared with the same time period in 2025. Therapeutic devices led industry growth, followed by non-imaging diagnostic, imaging, and lab equipment and tools. However, growth was highly concentrated among commercial leaders, highlighting a widening performance gap across the industry.

“MedTech has rebounded from YTD June lows and has underperformed the broader markets in 2026. The sector has continued to demonstrate resiliency, with record revenue financing and strong M&A activity setting the stage for a bright future,” says John Babitt, EY Global MedTech Leader. “The broader sector players are at a turning point where discipline is essential to convert innovation into profitable growth.”

Other key findings include:

MedTech financing reached a record US$63 billion for the year ended June 30, 2026, up 87% year over year – the highest seen in the last decade. Together, initial public offerings and debt accounted for around 80% of total capital raised, indicating that recovery has been driven primarily by public-market reopening and strategic balance sheet financing rather than broad-based funding strength.MedTech M&A reached its highest level in more than a decade, with total disclosed deal value surging to roughly US$130 billion. However, this recovery was driven by a limited number of blockbuster transactions.Innovation remains at the core of MedTech’s heartbeat, with growth largely driven by a breakout group of high-performing, high-differentiation, high-innovation strategic leaders. Companies that delivered both high R&D productivity and EBIT margin expansion generated an average total shareholder return of approximately 13.8%.AI in MedTech is observing a transformation, with intelligence being deeply embedded into devices and the care pathways around them. Hardware design, clinical evidence and manufacturing quality will remain fundamental and are increasingly being complemented by the quality of the algorithms, data and digital services surrounding the product.Venture capital fundraising remained resilient in 2026, with overall activity skewed toward earlier-stage innovation, highlighting improved investment activity and continued investor conviction in differentiated technologies addressing significant unmet clinical needs.

“MedTech is entering a new era of growth, and today’s challenges are the catalyst for the industry’s next transformations,” says Diana Hoff, EY Americas Life Sciences Sector Leader. “As companies navigate margin pressure, supply chain risk and global trade uncertainty, the leaders of the next decade will be those that embrace AI, make more deliberate portfolio choices and build productive, resilient operating models that turn innovation into sustained growth and value.”

Looking ahead, MedTechs that maintain innovation while also building conviction across capital allocation and portfolio optimization will be best positioned to set the pace of the pulse of the industry in the years to come.

To read Pulse of the MedTech Industry, please visit https://www.ey.com/en_us/life-sciences/pulse-of-medtech-industry-outlook?WT.mc_id=14001805&AA.tsrc=pr.

About EY
EY is building a better working world by creating new value for clients, people, society and the planet, while building trust in capital markets.

Enabled by data, AI and advanced technology, EY teams help clients shape the future with confidence and develop answers for the most pressing issues of today and tomorrow.

EY teams work across a full spectrum of services in assurance, consulting, tax, strategy and transactions.

Fueled by sector insights, a globally connected, multidisciplinary network and diverse ecosystem partners, EY teams can provide services in more than 150 countries and territories.

All in to shape the future with confidence.

EY refers to the global organization, and may refer to one or more, of the member firms of Ernst & Young Global Limited, each of which is a separate legal entity. Ernst & Young Global Limited, a UK company limited by guarantee, does not provide services to clients. Information about how EY collects and uses personal data and a description of the rights individuals have under data protection legislation are available via ey.com/privacy. EY member firms do not practice law where prohibited by local laws. For more information about our organization, please visit ey.com.

Ernst & Young LLP is a client-serving member firm of Ernst & Young Global Limited operating in the US.

About EY Consumer and Health
The rise of the empowered consumer, coupled with technology advancements and the emergence of digitally focused entrants, is changing every aspect of health and care delivery. To retain relevancy in today’s digitally focused, data-infused ecosystem, all participants in healthcare today must rethink their business practices, including capital strategy, partnering and the creation of patient-centric operating models.

The EY Consumer and Health architecture brings together a worldwide network of 34,000 professionals to build data-centric approaches to customer engagement and improved outcomes. We help our clients deliver on their strategic goals, design optimized operating models and form the right partnerships so they may thrive today and succeed in the health systems of tomorrow. We work across the ecosystem to understand the implications of today’s trends, proactively finding solutions to business issues, and to seize the upside of disruption in this transformative age.

Media contact: Carol Piering, carol.piering@ey.com 

View original content to download multimedia:https://www.prnewswire.com/news-releases/ey-pulse-of-the-medtech-industry-report-2026-blockbuster-performers-and-innovation-drive-record-medtech-industry-growth-302910276.html

SOURCE EY

Continue Reading

Technology

CollectivIQ Introduces GigaBrain, Giving Enterprises a Shared Brain That Gets Smarter as Employees Work

Published

on

By

New Enterprise Intelligence Layer Turns the Collective Learnings of AI Agents Into Secure, Usable Organizational Knowledge

BOSTON, Oct. 21, 2026 /PRNewswire/ — CollectivIQ, the collective intelligence platform built to give employees more honest AI insights and digital teammates that put its intelligence to work, today announced the availability of GigaBrain, a new shared intelligence layer that enables organizations to capture, connect, and use the knowledge accumulated by employees and their Digital Direct Reports (DDRs), which are specialized AI teammates that work for people much like human direct reports do. Every company has valuable knowledge that lives outside its formal systems, across various tools, residing in employees’ heads, embedded in conversations, and lodged in disparate company applications. GigaBrain is designed to make that collective intelligence available to the organization and its employees.

As employees work with their Digital Direct Reports, those AI teammates develop context about their work, including projects, processes, responsibilities, relationships, and preferences. With GigaBrain, those individual learnings can contribute to a shared enterprise memory, allowing knowledge developed in one part of an organization to make AI more useful across the business. The result is an enterprise AI environment that gets smarter through use. Rather than requiring employees to repeatedly find, upload or explain the same information, GigaBrain gives employees and their Digital Direct Reports access to relevant organizational context when they need it.

When a sales representative’s DDR learns the intricacies of a customer’s procurement process, including approval requirements, key decision-makers, and purchasing timelines, that knowledge can automatically become available to other team members, subject to appropriate access permissions. When the customer reaches out for help, the team will already have the context needed to navigate the relationship effectively, without asking the customer to repeat information or relying on a manual handoff.

“Companies are collectively spending billions to bring intelligence to their employees, but very little of that investment makes the company itself smarter,” said John Davie, CEO of CollectivIQ. “The breakthrough isn’t just giving every employee an AI teammate, it’s making sure what those employees and AI teammates learn becomes an advantage for the entire organization. GigaBrain turns everyday work into intelligence that compounds across the enterprise.”

While enterprise AI platforms such as Microsoft Copilot and Glean help employees access organizational information, GigaBrain is designed to capture knowledge that emerges through employees’ day-to-day interactions with their DDRs, including insights that may never be formally documented. GigaBrain creates an organizational knowledge layer that can connect what employees and their Digital Direct Reports learn through everyday work, giving AI access to relevant internal context alongside the broader knowledge available from large language models.

GigaBrain was built to provide a source of enterprise knowledge that Digital Direct Reports can draw upon as they work, including the ability to trace information back to its source, giving employees greater visibility into where organizational knowledge came from, and helping AI work from relevant company context. Employees do not need to manually document every useful insight for the system to become more valuable. As they collaborate with their Digital Direct Reports, relevant knowledge can become part of the enterprise intelligence available to other authorized AI teammates.

GigaBrain is also designed for the realities of enterprise information governance, as employees can use an incognito mode when working with information that should not contribute to shared organizational memory, giving users a way to keep sensitive or confidential interactions out of GigaBrain.

GigaBrain expands CollectivIQ’s vision for Digital Direct Reports beyond individual AI productivity, allowing the knowledge developed through that work to become part of a broader organizational intelligence layer. Together, they give companies a foundation for AI that does more than answer questions. CollectivIQ’s ecosystem can learn how an organization works, retain what it learns and make that knowledge useful across the enterprise.

GigaBrain is available through the CollectivIQ platform. For more information, visit www.collectiviq.ai.

About CollectivIQ

CollectivIQ is the collective intelligence platform built to give employees more accurate AI insights and teammates that put its intelligence to work. Founded by the leadership team behind Buyers Edge Platform, CollectivIQ was built to bring accountability, action, and economic alignment to enterprise AI adoption. Learn more at www.collectiviq.ai.

View original content to download multimedia:https://www.prnewswire.com/news-releases/collectiviq-introduces-gigabrain-giving-enterprises-a-shared-brain-that-gets-smarter-as-employees-work-302915537.html

SOURCE CollectivIQ

Continue Reading

Technology

Pactum Launches Intake Agent, Cutting Purchase Request Cycle Time by 90%

Published

on

By

New AI agent replaces complicated purchase forms and repeated follow-ups by completing and checking every request before it is submitted, inside Microsoft Teams, Coupa, and SAP Ariba.

MOUNTAIN VIEW, Calif., Oct. 21, 2026 /PRNewswire/ — Pactum, the most advanced agentic AI platform for enterprise autonomous procurement execution, today announced the launch of its Intake Agent, which lets employees describe what they need to buy in plain language. The agent turns each request into a complete, correctly coded requisition and checks it against company buying policies before it is submitted.  Available now in Microsoft Teams, Coupa, and SAP Ariba, the Intake Agent connects with Pactum’s other agents to enable end-to-end autonomous indirect procurement. A purchase can draw on an existing contract or move to autonomous sourcing and negotiation, with a human buyer handling requests that require judgment.

The launch extends Pactum’s growing portfolio of AI agents to the start of indirect procurement, covering purchases such as software, office equipment, and professional services. It brings Pactum’s co-founders’ vision of procurement run with AI agents from the first request through sourcing and negotiation into operation. Procurement teams set the buying rules once, and the agent applies them to every request, whatever its value.

“Procurement teams can now run indirect procurement with full autonomy while remaining in control and managing the exceptions,” said Kaspar Korjus, Co-Founder and CEO of Pactum. “Our Intake Agent helps resolve questions earlier so requests can move forward with less back-and-forth and teams can focus on the decisions that need their expertise.”

For employees, finding an approved supplier or selecting the right accounting code can require expertise across procurement, finance, operations, and IT teams. Missing or incorrect information can lead to rejected requisitions and repeated follow-ups, leaving buyers to focus on correcting forms instead of focusing on supplier relationships and commercial decisions. Review queues can stretch from days to weeks.

With Pactum Intake, employees describe what the business needs, whether goods or services of any complexity, and can provide supporting documents such as a supplier quote. The agent uses the request and relevant documents to identify the best procurement category and complete the accounting and supplier details. It asks only the follow-up questions needed to complete the requisition. Once the request is checked, it is handed off to another Pactum digital worker to autonomously source and negotiate for better pricing and terms where required.

“Building software that assists procurement professionals is relatively easy. Building software that runs the whole process on its own, from the first request to the final purchase, is much harder,” said Kristjan Korjus, Co-Founder and Chief Scientist at Pactum. “It is the difference between driver assistance and a car with no one behind the wheel. Most procurement AI still needs a buyer at the wheel for every request. Our AI agents take the request all the way to the purchase on their own, and it is remarkable to watch them pass the work from one agent to the next.”

The launch follows Pactum’s Requisition Alignment Agent surpassing one million requisition checks, which validates purchase requests against company buying policies, existing contracts, and approved suppliers. Intake builds on this foundation in policy enforcement by connecting employee requests with agents that carry out sourcing and negotiation.

For more information about Pactum Intake, visit https://pactum.com/procurement-agents/intake.     

About Pactum:

Since 2019, Pactum has been leading the shift to autonomous procurement. Its AI agents check every purchase request against a company’s policies, contracts and approved suppliers, source and negotiate with suppliers in more than 40 languages, and work inside Coupa and SAP Ariba. Pactum agents are relied on by more than 60 of the world’s largest enterprises. To learn more, visit www.pactum.com.

View original content to download multimedia:https://www.prnewswire.com/news-releases/pactum-launches-intake-agent-cutting-purchase-request-cycle-time-by-90-302915539.html

SOURCE Pactum

Continue Reading

Technology

Crush Security Launches Crush Dollar Exposure, Turning Cyber Risk Into Dollars and Showing Which Security Investments Reduce It Most

Published

on

By

New financial risk intelligence capability uses FAIR-informed modeling, Monte Carlo analysis and security data to help CISOs and CFOs quantify cyber exposure, prioritize remediation and communicate financial risk to executive leadership.

SCOTTSDALE, Ariz., Oct. 21, 2026 /PRNewswire/ — Crush Security today announced the launch of Crush Dollar Exposure, a new capability within its cybersecurity intelligence platform that translates cyber risk into financial exposure and helps organizations identify which security improvements can deliver the greatest reduction in potential financial loss.

For years, cybersecurity teams have measured their environments through vulnerabilities, risk scores, compliance percentages and control gaps. While valuable to security operations, those measurements often fail to answer the fundamental questions that executives and boards need answered:

How much could our cybersecurity weaknesses cost the business, and where should we invest to reduce that exposure?

Crush Dollar Exposure is designed to answer those questions by connecting an organization’s security posture, control coverage, threat intelligence and industry financial loss data to a quantitative view of cyber risk. The result is a financial perspective that enables security and business leaders to evaluate potential losses, compare remediation priorities and make more informed investment decisions.

From Technical Risk Scores to Financial Decisions

Traditional cybersecurity assessments often produce long lists of findings ranked by technical severity. But the most technically severe vulnerability is not necessarily the one that represents the greatest potential financial loss to the organization.

Crush Dollar Exposure changes the decision-making process by evaluating security gaps through their estimated contribution to financial risk. The capability provides four principal measurements:

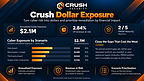
Annualized Financial Exposure: An estimate of potential annual cyber losses, expressed in dollars.Financial Exposure Relative to Revenue: A view of modeled cyber exposure in relation to the organization’s annual revenue, providing business context.Value-at-Risk Analysis: Potential loss thresholds at selected probability levels, supported by loss-exceedance curves that illustrate the range of possible financial outcomes.Financially Prioritized Remediation: Security control gaps ranked by their modeled contribution to financial exposure, helping teams identify where remediation may reduce the most risk.

Rather than simply reporting that a security control is missing or a vulnerability is critical, Crush Dollar Exposure helps organizations understand the potential financial consequences and prioritize corrective action accordingly.

Connecting Every Security Gap to Business Impact

One of the capability’s key differentiators is its ability to connect security control weaknesses to modeled loss scenarios and financial consequences.

For example, a security team evaluating investments in identity protection, endpoint security and vulnerability remediation can use the model to determine which weaknesses contribute most significantly to estimated financial exposure. This allows security leaders to move beyond asking which problem is technically most severe and begin asking which investment is likely to provide the greatest financial risk reduction.

The analysis also connects control gaps to underlying loss scenarios, helping organizations understand how multiple weaknesses may contribute to the same business risk. For CFOs and executive teams, this provides a more financially grounded way to evaluate cybersecurity spending. For CISOs, it creates a defensible framework for explaining security priorities and communicating their potential business impact.

Transparent, Reproducible Risk Modeling — Not a Black-Box AI Score

Crush Dollar Exposure uses a quantitative methodology informed by the Factor Analysis of Information Risk (FAIR) framework and Monte Carlo simulation to model possible financial losses.

The methodology incorporates security control coverage, industry-relevant threat activity, recognized adversary techniques, organizational characteristics and established financial loss reference data.

Unlike opaque risk-scoring approaches, the capability is designed to make the assumptions, data inputs and modeled loss scenarios underlying its financial estimates visible and reviewable. Although Crush Security’s broader platform includes Cassandra, its AI-powered security advisor, the financial risk calculations themselves rely on defined quantitative modeling rather than generative AI.

The capability distinguishes between uncertainty in modeled financial outcomes and confidence in the quality of supporting data, helping executives understand both the estimated exposure and the limitations of the underlying analysis. This transparency is intended to support repeatable analysis, auditability and more defensible conversations with boards, regulators and financial stakeholders.

Giving CISOs and CFOs a Common Language

“Cybersecurity leaders are constantly asked to justify their budgets, but we’re still presenting information to boards that doesn’t directly answer the questions they’re asking,” said Josh Jones, CEO and Co-Founder of Crush Security. “Boards don’t just want to know how many vulnerabilities you have or how many security tools you’ve deployed. They want to understand what the risk could cost the business, where their money is going, and whether those investments are making a measurable difference.”

“With Crush Dollar Exposure, we’re connecting cybersecurity decisions to financial outcomes. Our goal is to give every CISO the ability to walk into a board meeting and explain their organization’s estimated financial exposure, identify the gaps driving it, and show which actions have the greatest potential to reduce that risk.” -Joshua Jones, CEO-

Built on the Crush Security Intelligence Platform

Crush Dollar Exposure extends Crush Security’s intelligence platform, which brings together vendor, control, compliance and threat data to support security investment decisions.

Powered by Cassandra, the platform helps organizations identify coverage gaps, compare technology and vendors, and optimize cybersecurity spending.

Risk calculations are performed within each customer’s data environment, with customer-specific information remaining within its designated security boundary. Anonymized and aggregated industry reference information supports comparative risk modeling.

Availability

Crush Dollar Exposure is available now within the Crush Security platform. Organizations interested in quantifying their financial cyber exposure, evaluating remediation priorities or scheduling a demonstration can visit www.CrushSecurity.com. Access information is available directly from Crush Security.

About Crush Security

Crush Security is a veteran-owned cybersecurity technology and advisory company headquartered in Scottsdale, Arizona.

Its proprietary intelligence platform, advisory services and cybersecurity procurement data help customers make data-driven technology purchasing decisions leveraging Crush Security’s resell capabilities.

Cassandra, its AI-powered advisor, unifies security, vendor and compliance intelligence to identify gaps, optimize investments, quantify risk and evaluate solutions to shorten the decision time and accuracy for each project.

Crush Security’s core intelligence platform is currently included at no separate subscription cost with eligible customer engagements.

Website: www.CrushSecurity.com

View original content to download multimedia:https://www.prnewswire.com/news-releases/crush-security-launches-crush-dollar-exposure-turning-cyber-risk-into-dollars-and-showing-which-security-investments-reduce-it-most-302914088.html

SOURCE Crush Security Group Inc

Continue Reading

Trending