Technology
Grounded AI Is Only Half the Answer for Third-Party Insurance Compliance, Says illumend CEO Kristen Nunery
Published
1 hour agoon
By
Nunery advocates for AI systems that evaluate Certificates of Insurance against an organization’s specific requirements, reason across connected documents, produce traceable decisions, and preserve human oversight
Key Takeaways
Grounding AI in an organization’s specific insurance requirements is essential, but it is only part of what reliable certificate of insurance compliance requires.AI systems must reason across contracts, certificates of insurance, endorsements, schedules, amendments, and exceptions to evaluate the complete body of evidence.Accurate document extraction does not guarantee an accurate compliance decision because compliance depends on the relationships among requirements and supporting documents.Every AI-supported compliance determination should be traceable, explainable, and subject to human approval so it can withstand an audit, dispute, or claim.Organizations evaluating grounded AI compliance platforms should measure both false passes that leave risk uncovered and false failures that create unnecessary work.
INDIANAPOLIS, Sept. 16, 2026 /PRNewswire/ — Kristen Nunery, CEO of illumend and founder of myCOI, is calling on business leaders to demand more from grounded artificial intelligence (AI) in Certificate of Insurance (COI) compliance. Nunery details her point of view in a new article titled “Grounding Is Half the Answer in COI Compliance.” The issue affects organizations that rely on vendors, contractors, tenants, franchisees, and other third parties to maintain contractually required insurance coverage, including businesses in construction, commercial real estate, retail and franchising, and government.
Grounded AI is an approach that bases its outputs on defined, authoritative information rather than relying solely on the general knowledge acquired during model training. In COI compliance, that information includes an organization’s contracts, leases, insurance requirements, vendor classifications, required endorsements and approved exceptions.
Nunery’s position is that grounding AI in an organization’s insurance requirements provides a standard for evaluating compliance, but it does not provide sufficient evidence to make a reliable decision. AI systems must also connect information across contracts, certificates, endorsements, schedules, and amendments—and explain how that evidence supports each determination.
Modern AI can accurately extract policy numbers, coverage limits, carriers, and expiration dates from certificates. The distinction, Nunery argues, is that document extraction determines what an insurance document says, while compliance analysis determines whether the full body of evidence satisfies the requirements for a specific vendor, contract, project, or business relationship.
“COI compliance is a document-relationship problem before it is a document-reading problem,” Nunery said. “An AI system can read every individual document correctly and still reach the wrong conclusion if it cannot understand how the agreement, certificate, policy, endorsement, and schedule relate to one another.”
What Grounded AI Means for COI Compliance
Grounded AI is anchored to a defined source of truth rather than relying on general information absorbed during model training. In COI compliance, the relevant source of truth includes an organization’s contracts, leases, insurance requirements, vendor classifications, project standards, required endorsements, and approved exceptions.
Grounding changes the question the system answers. An ungrounded system may assess whether a vendor appears adequately insured, even though “adequately insured” has no universal definition. A grounded system evaluates whether submitted evidence satisfies the requirements governing that specific third-party relationship.
The key difference is that grounded AI evaluates insurance evidence against requirements established by the organization rather than relying on a generalized model-generated standard of adequate coverage.
“Grounding gives the AI the standard instead of asking it to invent one,” Nunery said. “A system that cannot tell you where its definition of compliant came from does not really have one.”
Why Is Grounded AI Only Half the Answer?
Even a system perfectly grounded in an organization’s requirements can reach the wrong decision if it fails to connect all relevant evidence.
For example, a certificate may indicate that additional insured coverage is present while an attached endorsement covers only ongoing operations. If the governing agreement also requires completed operations coverage, approving the vendor based solely on the certificate could leave the organization exposed if a claim arises after the work has ended.
Every document in that example could be read accurately. The incorrect decision would result from failing to connect the certificate and endorsement with the requirement established by the contract.
For businesses, this means accurate extraction is necessary but insufficient. A reliable COI compliance system must determine how information in one document changes, supports, limits, or contradicts information in another.
“Cross-document reasoning tells the system what the complete evidence means, while grounding tells it which requirements that evidence must satisfy,” Nunery said. “Remove either one, and the resulting determination is a guess wearing a confident tone.”
Nunery advocates for grounded AI systems that evaluate related insurance documents as one body of evidence. A system should determine whether a required endorsement exists, applies to the correct policy, names the appropriate legal entity or project, and satisfies the governing contract. It should also recognize when amendments, schedules, project requirements, or approved exceptions change the compliance decision.
In practical terms, grounding establishes the compliance standard, while cross-document reasoning determines whether the available evidence actually meets that standard.
Why Traceable AI Decisions Matter in COI Compliance
Nunery argues that every AI-supported compliance determination should identify which requirement applied, which documents were evaluated, and why the system reached its conclusion.
“A compliance determination that cannot be reconstructed is not defensible, however confident the system sounded when it made it,” Nunery said. “Auditability should be treated as a fundamental requirement for grounded AI, not an optional reporting feature.”
Traceability becomes critical during audits, contractual disputes, and claims. A confidence score or pass-fail label does not establish that the system applied the correct agreement, reviewed the relevant endorsements, considered approved exceptions, or evaluated the complete evidence.
A traceable COI compliance decision should allow a reviewer to reconstruct the path from the governing requirement to the supporting documents and the resulting determination.
Human oversight must also remain part of the process. AI can accelerate reviews and identify potential deficiencies, but a person should approve a determination before a third party is declared compliant—particularly when evidence is incomplete, policy language is unusual, or an exception applies.
Seven Questions to Ask a Grounded AI Compliance Vendor
Nunery recommends focusing less on the underlying AI model and more on the requirements, evidence, and controls surrounding it. Buyers should ask:
Who defines “compliant” in the system?Are requirements configured before the system operates at scale?Does the system connect certificates with contracts, endorsements, and schedules?Can it distinguish missing evidence from deficient coverage?Is every determination supported by documented reasoning?Does a person approve the decision before a vendor is declared compliant?Which capabilities are available today rather than planned for the future?
Nunery also recommends measuring both false passes and false failures. A false pass leaves uncovered risk in an organization’s portfolio, while a false failure creates unnecessary work by prompting teams to pursue vendors that were not out of compliance.
The two measures reveal different types of system error: false passes indicate potential risk exposure, while false failures indicate unnecessary operational work and third-party friction.
“A system that reports only one of those numbers is telling you half of what happened,” Nunery said.
How illumend Uses Grounded AI for COI Compliance
illumend is an AI-powered third-party insurance compliance and risk management platform backed by myCOI’s institutional data foundation. Nunery founded myCOI more than 16 years ago, and the company’s experience includes reviewing 45 million documents, managing 1.2 million agreements, and identifying 2 million coverage gaps before they became claims.
During onboarding, illumend configures an organization’s insurance requirements based on standards derived from its contracts and leases. The platform then evaluates submitted evidence against the defined requirements, reviews endorsements with each submission, identifies specific deficiencies, manages renewals, and documents the reasoning behind each determination. A person signs off before a third party is notified of its compliance.
The workflow is designed to connect four components of a compliance decision: the organization’s requirements, the submitted insurance evidence, the reasoning used to evaluate that evidence, and human approval of the final determination.
“Grounding AI in an organization’s requirements is the right place to start, but it is only half the answer,” Nunery said. “Risk and compliance leaders should demand systems that understand the complete compliance picture, apply the correct requirements consistently, and produce decisions that can withstand scrutiny when an audit, dispute, or claim occurs.”
Frequently Asked Questions
How should an organization prepare its insurance requirements before implementing grounded AI for COI compliance?
Organizations should first document the requirements contained in their contracts and leases, including differences by vendor type, project, division, and jurisdiction. They should also identify required endorsements and approved exceptions. The goal is to establish a defined source of truth before AI begins making compliance evaluations. During onboarding, illumend configures each organization’s requirements so the platform evaluates evidence against its actual standards rather than assumptions generated by an AI model.
How should grounded AI distinguish missing insurance evidence from deficient coverage?
Grounded AI should treat missing evidence and deficient coverage as separate compliance states. Missing evidence means the system lacks the documentation needed to complete an evaluation; deficient coverage means the available evidence does not satisfy a defined requirement. The distinction matters because missing documentation does not, by itself, prove that the underlying coverage is deficient. The illumend platform identifies deficiencies with sufficient specificity for third parties to understand what needs to be corrected, without treating every documentation gap as proof of noncompliance.
What records should an AI-powered COI compliance platform maintain for audits and claims?
An AI-powered compliance platform should record the applicable requirement, the documents evaluated, the deficiencies identified, and the reasoning supporting each determination. Those records help an organization reconstruct how a decision was made during an audit, contractual dispute, or claim. illumend maintains requirements, documents, deficiencies, renewals, resolution activities, and decision reasoning within a single connected workflow.
How can risk leaders determine whether a grounded AI compliance platform is working accurately?
Business leaders should evaluate both false passes and false failures rather than rely on a single accuracy percentage. False passes leave potential coverage gaps in the organization’s portfolio, while false failures create unnecessary work and vendor friction. A meaningful accuracy assessment should therefore measure both risk-related errors and operational errors. illumend recommends assessing whether a platform consistently applies the correct requirements, evaluates the complete evidence, and produces decisions that people can review and reconstruct.
What is the difference between grounded AI and cross-document reasoning in COI compliance?
Grounded AI establishes the requirements an insurance submission must satisfy, while cross-document reasoning evaluates how contracts, certificates, endorsements, schedules, amendments, and exceptions work together as evidence. Reliable COI compliance requires both: grounding defines the standard, and cross-document reasoning determines whether the evidence meets it.
Why is document extraction alone not enough for COI compliance?
Document extraction identifies information such as policy numbers, limits, carriers, and expiration dates, but compliance depends on how that information relates to contractual requirements and other insurance documents. A system can extract every field correctly and still make an incorrect compliance determination if it fails to evaluate those relationships.
To read Nunery’s full article, visit https://www.linkedin.com/pulse/grounding-half-answer-coi-compliance-kristen-nunery-wxaye/.
About illumend
Founded in 2025, illumend™ is the AI-powered platform redefining how businesses manage third-party insurance compliance and risk. Backed by myCOI, the leader in third-party insurance compliance management with more than 16 years of expertise, illumend reimagines compliance by guiding every step of the process—from document review and expiration tracking to risk flagging, communication, and resolution—within one intuitive system. Built on myCOI’s institutional foundation—having processed more than 45 million documents, managed over 1.2 million agreements, cleared more than 750,000 third-party partners, and identified more than two million coverage gaps before claims—illumend brings this depth of compliance intelligence into an AI-native platform. At its core is Lumie, illumend’s conversational AI guide that reads complex insurance documents, flags issues in real time, and explains them in language anyone can act on. To learn more, visit https://www.illumend.ai.
Media contact:
Michael Tebo
Gabriel Marketing Group (for illumend)
Phone: 571-835-8775
Email: michaelt@gabrielmarketing.com
View original content to download multimedia:https://www.prnewswire.com/news-releases/grounded-ai-is-only-half-the-answer-for-third-party-insurance-compliance-says-illumend-ceo-kristen-nunery-302879454.html
SOURCE illumend
You may like
Technology
OpenText, Cohere Partner to Combine Trusted Data with Agentic AI
Published
23 minutes agoon
September 16, 2026By
Partnership combines OpenText’s trusted data and context with Cohere’s North platform and models to help organizations build, connect, and orchestrate agentic AI from pilot to production
MONTREAL, Sept. 16, 2026 /CNW/ — OpenText Corporation (NASDAQ: OTEX) (TSX: OTEX), a global leader in data management and context for enterprise AI, and Cohere, the world’s leading sovereign AI company, today announced a strategic partnership at the ALL IN AI conference to bring trusted agentic AI to governments and regulated industries.
Together, OpenText and Cohere provide complementary layers of the AI stack for the agentic enterprise. As the data and context layer, OpenText unlocks enterprise data, including unstructured, operational and transactional data, and gives agentic AI the context it needs. Cohere provides the application and orchestration layer through North, its secure, privately deployable agentic AI platform, together with its cutting-edge enterprise AI models for powering complex automations. Clients have the choice of where it all runs: on-premises, or in a private, public, or sovereign cloud depending on their security, data, and deployment requirements.
“Data is not the supporting act; it is what gives agentic AI the context it needs to perform,” said Ayman Antoun, Chief Executive Officer, OpenText. “OpenText brings the data and context layer, while Cohere brings the orchestration and models that turn that data into agentic AI that acts with purpose. Together, we give clients what they need to build the agentic enterprise.”
Expected to reach clients in early 2027, the OpenText and Cohere agentic solution is purpose built for governments and organizations in highly regulated sectors, where AI agents must reason over trusted data and act across systems without sacrificing control over data location, security, or deployment. OpenText’s data and context layer already runs inside the world’s top 20 federal governments, along with healthcare systems, financial institutions, insurers, and global supply chains, through its Content, Business Network, IT Operations Management (ITOM), and Cybersecurity solutions.
“Enterprises and governments need AI that can work with their most important data while keeping them in control of where that data lives and how it is used,” said Aidan Gomez, Co-founder and CEO of Cohere. “By bringing North and our models together with OpenText’s trusted data and context, we’re giving organizations a secure path to move agentic AI from pilot to production and put it to work across the systems and workflows their teams rely on every day.”
OpenText brings clients a world-class ecosystem of partners that together deliver the full AI stack they need to deploy agentic AI. The OpenText and Cohere partnership will include product development, integration of Cohere’s agentic platform and models into OpenText Aviator AI agents, coordinated go-to-market execution, and a strategic reseller relationship through SOLEX, enabling OpenText to offer Cohere-supported solutions both on-premises and through OpenText Cloud.
Two Canadian AI Leaders With Global Reach
OpenText was founded in Canada in 1991 and serves more than 120,000 enterprise clients in 180 countries. Cohere was founded in Toronto in 2019 and is the world’s leading sovereign AI company building cutting-edge foundation models and end-to-end AI products for enterprise and public sector organizations. Together, the companies extend a common foundation in trust and security to regulated markets worldwide, where deployment choice and control over data matter most.
About OpenText
OpenText™ is a global leader in data management for enterprise AI, helping organizations protect, govern, and activate their data with confidence. Our technologies turn data into information with context to form the knowledge base for enterprise AI. Learn more at www.opentext.com.
About Cohere
Cohere, founded in 2019, is the world’s leading sovereign AI company building foundations models and end-to-end AI products to solve real-world business problems. Cohere partners with organizations to deliver seamless integration, customization and user-friendly solutions. Its all-in-one platform provides maximum security, privacy and deployment flexibility across clouds, private environments and on-premises. Headquartered in Toronto and San Francisco, Cohere operates additional offices in London, New York, Montreal, Paris, and Seoul, serving customers worldwide. The company has raised ~1.6 billion USD from strategic investors (AMD Ventures, Salesforce Ventures, Oracle, Cisco), institutional investors (Radical Ventures, Inovia Capital, PSP Investments, HOOPP, BDC, Nexxus), and AI pioneers including Geoffrey Hinton, Fei-Fei Li, Pieter Abbeel, and Raquel Urtsaun. For more information, visit Cohere.com.
Cautionary Statement Regarding Forward-Looking Statements
Certain statements in this press release may contain words considered forward-looking statements or information under applicable securities laws, including statements about Open Text Corporation (“OpenText” or the “Company”) regarding the anticipated benefits of the partnership between OpenText and Cohere, product development, and integration of Cohere’s North platform and models into OpenText’s enterprise AI Aviator portfolio, coordinated go-to-market activities, and the expected timing and availability of integrated capabilities.
These statements are subject to important assumptions, risks and uncertainties that are difficult to predict, and the actual outcome may be materially different. OpenText’s assumptions, although considered reasonable by the company at the date of this press release, may prove to be inaccurate and consequently its actual results could differ materially from the expectations set out herein. For additional information with respect to risks and other factors which could occur, see OpenText’s Annual Report on Form 10-K, Quarterly Reports on Form 10-Q and other securities filings with the SEC and other securities regulators. Readers are cautioned not to place undue reliance upon any such forward-looking statements, which speak only as of the date made. Unless otherwise required by applicable securities laws, OpenText disclaims any intention or obligations to update or revise any forward-looking statements, whether as a result of new information, future events or otherwise. Further, readers should note that we may announce information using our website, press releases, securities law filings, public conference calls, webcasts and the social media channels identified on the Investors section of our website (https://investors.opentext.com). Such social media channels may include the Company’s or our CEO’s blog, X, formerly known as Twitter, account or LinkedIn account. The information posted through such channels may be material. Accordingly, readers should monitor such channels in addition to our other forms of communication.
OTEX-G
View original content to download multimedia:https://www.prnewswire.com/news-releases/opentext-cohere-partner-to-combine-trusted-data-with-agentic-ai-302880201.html
SOURCE Open Text Corporation
Technology
New BaaS Platform Bolt by Reseda Group Launches with First Fintech Partner TAPP Engine
Published
23 minutes agoon
September 16, 2026By
New platform signs TAPP Engine as first fintech leveraging Bolt to accelerate delivery of cash management solutions directly to MSUFCU as the Financial Institution of Record
EAST LANSING, Mich., Sept. 16, 2026 /PRNewswire/ — Reseda Group today announced the launch of Bolt by Reseda Group, a Banking-as-a-Service (BaaS) platform that enables financial institutions and fintech companies to bring innovative financial solutions to market faster through a secure, API and SDK-driven banking infrastructure with MSU Federal Credit Union (MSUFCU), as the Financial Institution of Record (FIoR). The platform’s first fintech partner, TAPP Engine, is leveraging Bolt to seamlessly connect its cash management solutions directly to MSUFCU as the FIoR, delivering fully branded, modern, embedded banking experiences to their customers.
Bolt delivers the infrastructure fintechs and financial institutions need to launch and scale new products while maintaining the trust, compliance, and security consumers expect. Through a comprehensive suite of APIs, SDKs (Software Development Kit), and software solutions, the platform supports modern digital banking experiences, including account opening, payments and money movement, debit card issuance, external account connectivity, and embedded finance capabilities.
Developed by Reseda Group and informed by the proven innovation experience of MSU Federal Credit Union (MSUFCU), Bolt combines the agility of modern BaaS infrastructure with the real-world expertise of a financial institution that has successfully built and deployed fintech solutions. The result is a secure, scalable platform that empowers fintechs and financial institutions to innovate together, accelerate time to market, and deliver new financial experiences to consumers with confidence.
“Speed to market is essential for both financial institutions and fintech innovators looking to meet evolving consumer expectations,” said Ben Maxim, Chief Operating Officer at Reseda Group and Chief Technology Officer at MSUFCU. “Bolt by Reseda Group was built to remove the barriers that often slow innovation by creating a secure, seamless bridge between fintech innovators and trusted financial institutions. With APIs, flexible integration options, and comprehensive banking infrastructure, we’re helping organizations bring new solutions and enhanced experiences to people today, not years from now.”
Bolt enables financial institutions to accelerate fintech partnerships, expand digital banking capabilities, introduce new deposit experiences, and power embedded finance solutions. For fintech companies, the platform provides the flexibility to focus on building transformative experiences without navigating the regulatory and operational complexities of becoming a licensed financial institution.
Through a governed framework, Bolt works with specific vendor partners to securely support Know Your Customer/Know Your Business (KYC/KYB) processes before new account opening begins. Once accounts are established, MSUFCU provides ongoing account monitoring, compliance oversight and identification of unusual account activity to support continued risk management. This shared responsibility model allows fintechs to focus on their customer experience and what they do best.
With Bolt, fintechs and financial institutions gain access to:
Speed to market: Accelerate product launches through streamlined API/SDK connectivity and pre-built banking capabilities.Complete banking infrastructure: Access onboarding, account management, payments, debit card services, and digital banking functionality through a single platform.Secure innovation: Leverage infrastructure designed with compliance, security, and operational resilience in mind.Scalable growth: Adapt financial offerings as consumer and business needs evolve without redesigning entire systems.Simplified integration: Use modern APIs, SDKs, webhooks, and flexible development tools to accelerate implementation.
As Bolt’s first fintech client, TAPP Engine is leveraging the platform to connect its cash management tools directly to the financial institutions holding its clients’ deposits. Bolt enables TAPP Engine to deliver a fully white-labeled private banking experience, allowing each TAPP client to offer a branded, seamless way to manage cash while keeping deposits with trusted credit unions.
“Bolt gives TAPP Engine the critical infrastructure to connect our cash management tools directly to the institutions holding our clients’ deposits,” said Will Dolan, President of TAPP Engine. “Its BaaS platform allows us to deliver a fully white-labeled private banking experience, so every TAPP client can offer a branded, seamless way to manage cash. Because those deposits sit with credit unions, we’re able to pair a premium experience with the trust and community focus that sets this offering apart.”
The launch of Bolt builds on Reseda Group’s vision to strengthen connections between people and their financial institutions through next-generation solutions. By bringing the operational experience of MSUFCU together with the innovation and agility of fintech partners, Bolt creates new opportunities for financial institutions and technology companies to collaborate, expand access to financial services and deliver greater value to the people and businesses they serve.
For more information about Bolt by Reseda Group, visit resedagroup.com/bolt.
About Reseda Group
Headquartered in East Lansing, Michigan, Reseda Group is a wholly owned credit union service organization of MSU Federal Credit Union (MSUFCU). Formed in 2021, Reseda Group changes the way people interact with their finances and how financial institutions engage with their consumers. By leveraging innovative products developed in-house and through its partnership ecosystem, Reseda Group is making financial technology and engagement solutions more accessible and approachable to the industry. Learn more at resedagroup.com.
About TAPP Engine
TAPP Engine modernizes capital formation, wealth management, and liquidity infrastructure for credit unions, community financial institutions, and regional financial institutions. Brokerage services are offered through TAPP Engine Securities, LLC. (“TES”). Digital Advisory services and technology offered through TAPP Engine Advisors, LLC (“TEA). Visit tappengine.com to learn more.
View original content to download multimedia:https://www.prnewswire.com/news-releases/new-baas-platform-bolt-by-reseda-group-launches-with-first-fintech-partner-tapp-engine-302879662.html
SOURCE Reseda Group
Technology
Ember Launches Mug 3, its Third-Generation Flagship Smart Mug
Published
23 minutes agoon
September 16, 2026By
Ember’s newest smart mug adds on-mug temperature control, dishwasher-safe design, and an included lid for extended battery life, helping customers elevate the everyday coffee and tea ritual
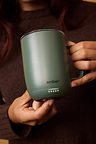
WESTLAKE VILLAGE, Calif., Sept. 16, 2026 /PRNewswire/ — Ember Technologies, the global leader in temperature-controlled drinkware, launched Ember Mug 3 today, the third generation of its flagship mug. Building on more than 10 years of market leadership, Mug 3 introduces several of the most requested improvements from Ember customers. For the first time, users can adjust their drinking temperature directly from the mug without opening the Ember app. Mug 3 is also top-rack dishwasher-safe, making cleaning it easier than ever, and every mug now includes a sipping lid that extends the battery life.
“Ember has leveraged new technology and innovation to make the new Mug 3 easier and more natural to use, all while maintaining its award-winning design,” said Matt Murray, CEO of Ember. “We listened to our user feedback when developing the new mug, and are excited to share it with the Ember community. If you are an existing Ember user, we think you will be delighted with the new features, and if you are a first-time user, we are excited to change the way you drink your coffee or tea every day.”
With the introduction of Mug 3, users can now set the temperature either on the mug itself or using the accompanying Ember app. Owners press the power button at the bottom of the mug to cycle through five temperature settings in preset five-degree increments, from 125 to 145 degrees Fahrenheit. The on-board temperature seamlessly syncs with the Ember app.
Ember improved the materials and manufacturing process for Mug 3 to make it top-rack dishwasher-safe while maintaining the same stainless steel and an FDA-compliant, ceramic-reinforced exterior and interior coating as previous Ember mugs. Caring for your Ember mug is now easier than ever.
Additionally, every Mug 3 now includes a sliding lid to help prevent spilling and keep a drink at its ideal temperature for up to three hours on a single charge, giving users even more time to savor their coffee and tea.
The Mug 3 ships in 10-ounce and 14-ounce sizes. The 10-ounce is available for $129 USD in black, white, and a new stainless model, while the 14-ounce is $149 USD and has eight color options: black, sage green, lavender, powder blue, salt blue, sandstone, white, and matcha green.
Ember Mug 3 is now available for purchase at ember.com and will be sold at Target, both online and in-store starting September 27. In October, it will also be available on Amazon.
About Ember Technologies
Ember Technologies is a global design-led temperature control brand and technology platform whose mission is to revolutionize the way people eat, drink, and live. Ember Technologies creates, designs, and develops temperature control products that offer people complete customization. The award-winning Ember Travel Mug and Ember Mug are the most advanced coffee mugs on the market, allowing individuals to set and maintain their preferred drinking temperature for hot beverages. For more information, visit ember.com and connect with us on Instagram, Facebook, and TikTok.
View original content to download multimedia:https://www.prnewswire.com/news-releases/ember-launches-mug-3-its-third-generation-flagship-smart-mug-302879860.html
SOURCE Ember Technologies, Inc.
OpenText, Cohere Partner to Combine Trusted Data with Agentic AI
New BaaS Platform Bolt by Reseda Group Launches with First Fintech Partner TAPP Engine
Ember Launches Mug 3, its Third-Generation Flagship Smart Mug
Send Rakhi to UK swiftly with UK Gifts Portal
Whiteboard Series with NEAR | Ep: 45 Joel Thorstensson from ceramic.network
New Gooseneck Omni Antennas Offer Enhanced Signals in a Durable Package
Why You Should Build on #NEAR – Co-founder Illia Polosukhin at CV Labs
Whiteboard Series with NEAR | Ep: 45 Joel Thorstensson from ceramic.network
NEAR End of Year Town Hall 2021: The Open Web World, MetaBUILD 2 Hackathon and 2021 recap
Trending
-
Technology2 days agoHexagon Creates A Constitution for AI, Adopted and Enforced on a Public Blockchain — and Anyone Can Check It
-
Coin Market4 days agoNvidia considers $10B investment in potential record Anthropic IPO: Reuters
-
Technology4 days agoLarry Ellison Cancels His Plan to Sell Oracle Stock
-
Technology5 days agoUrgentIQ Announces Strategic Growth Investment From Five Elms Capital
-
Technology4 days agoKrelva Accepted Into the HBS Foundry Bootcamp at Harvard Business School
-
Coin Market5 days agoTrading stocks against BONER is the latest trend for DeFi degens
-
Coin Market5 days agoBitcoin ETF outflows accelerate as investors pull $449M in three days
-
Coin Market5 days agoHyperliquid’s biggest risk is regulation, says Ran Neuner